Compliance meets
security intelligence.
Run ISO 27001, SOC 2, NIST CSF, and CMMC 2.0 with live signals from your cloud, your domain, and your suppliers, and a single score that tells you where you stand.
Product tour
What the platform actually looks like
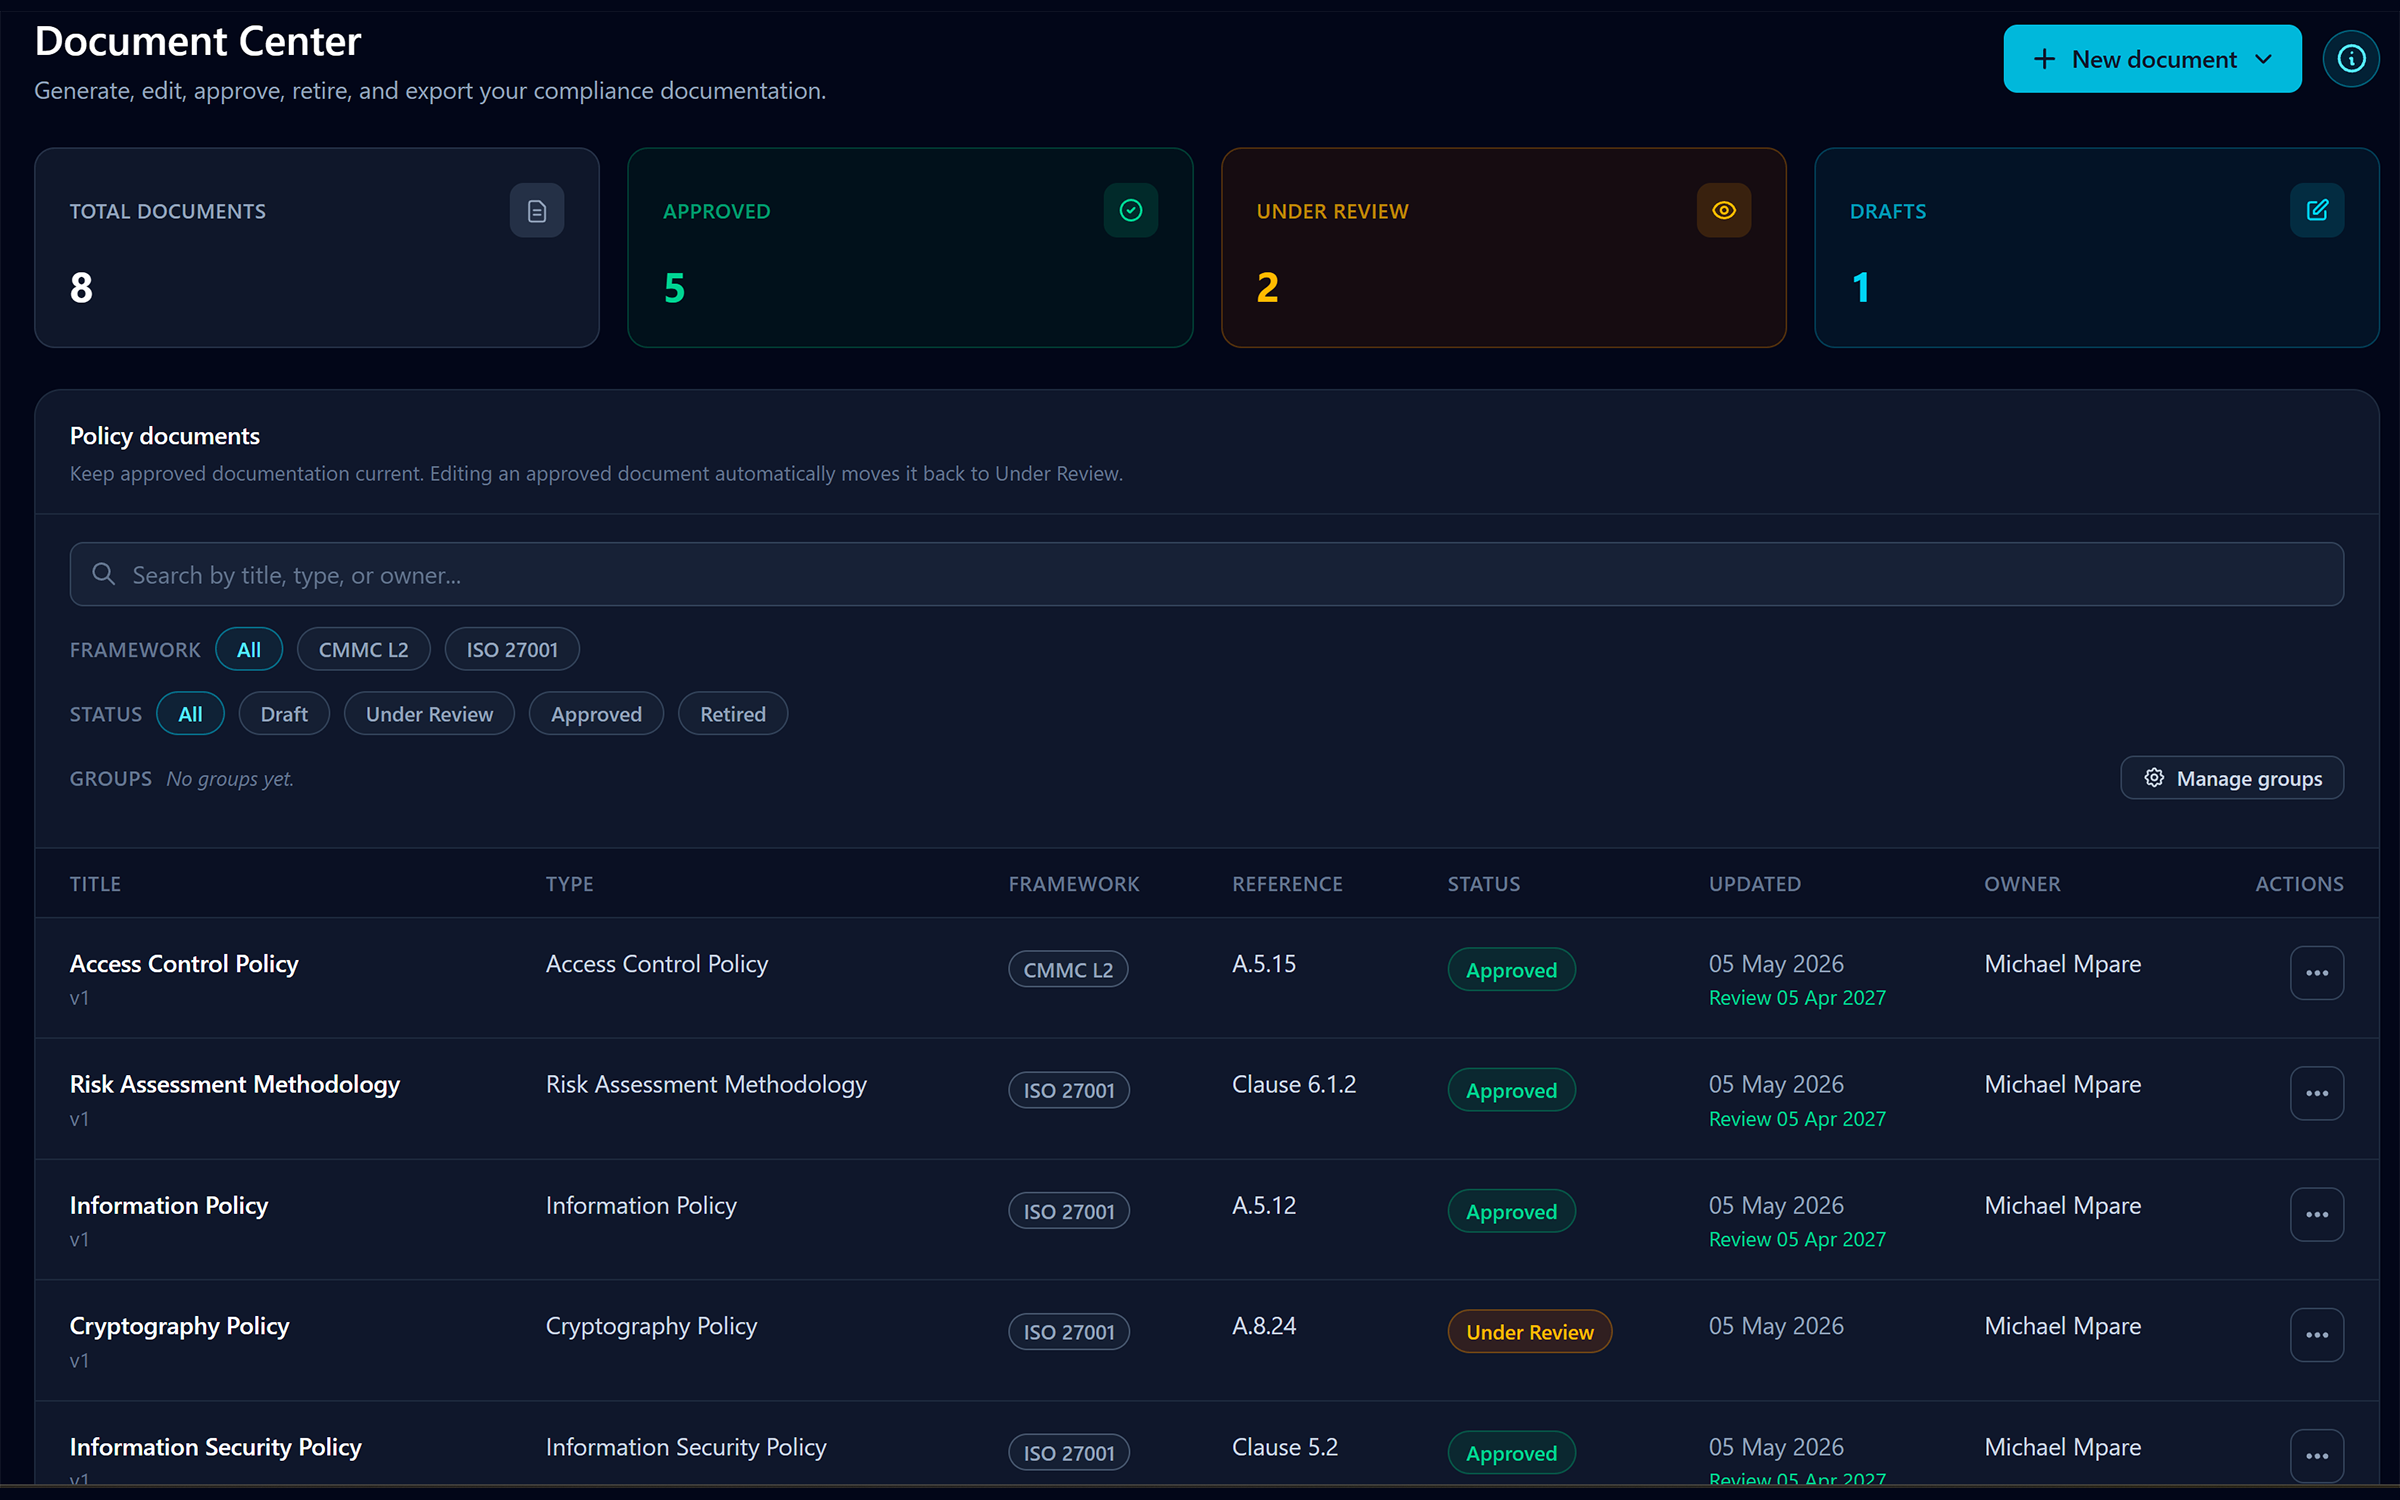
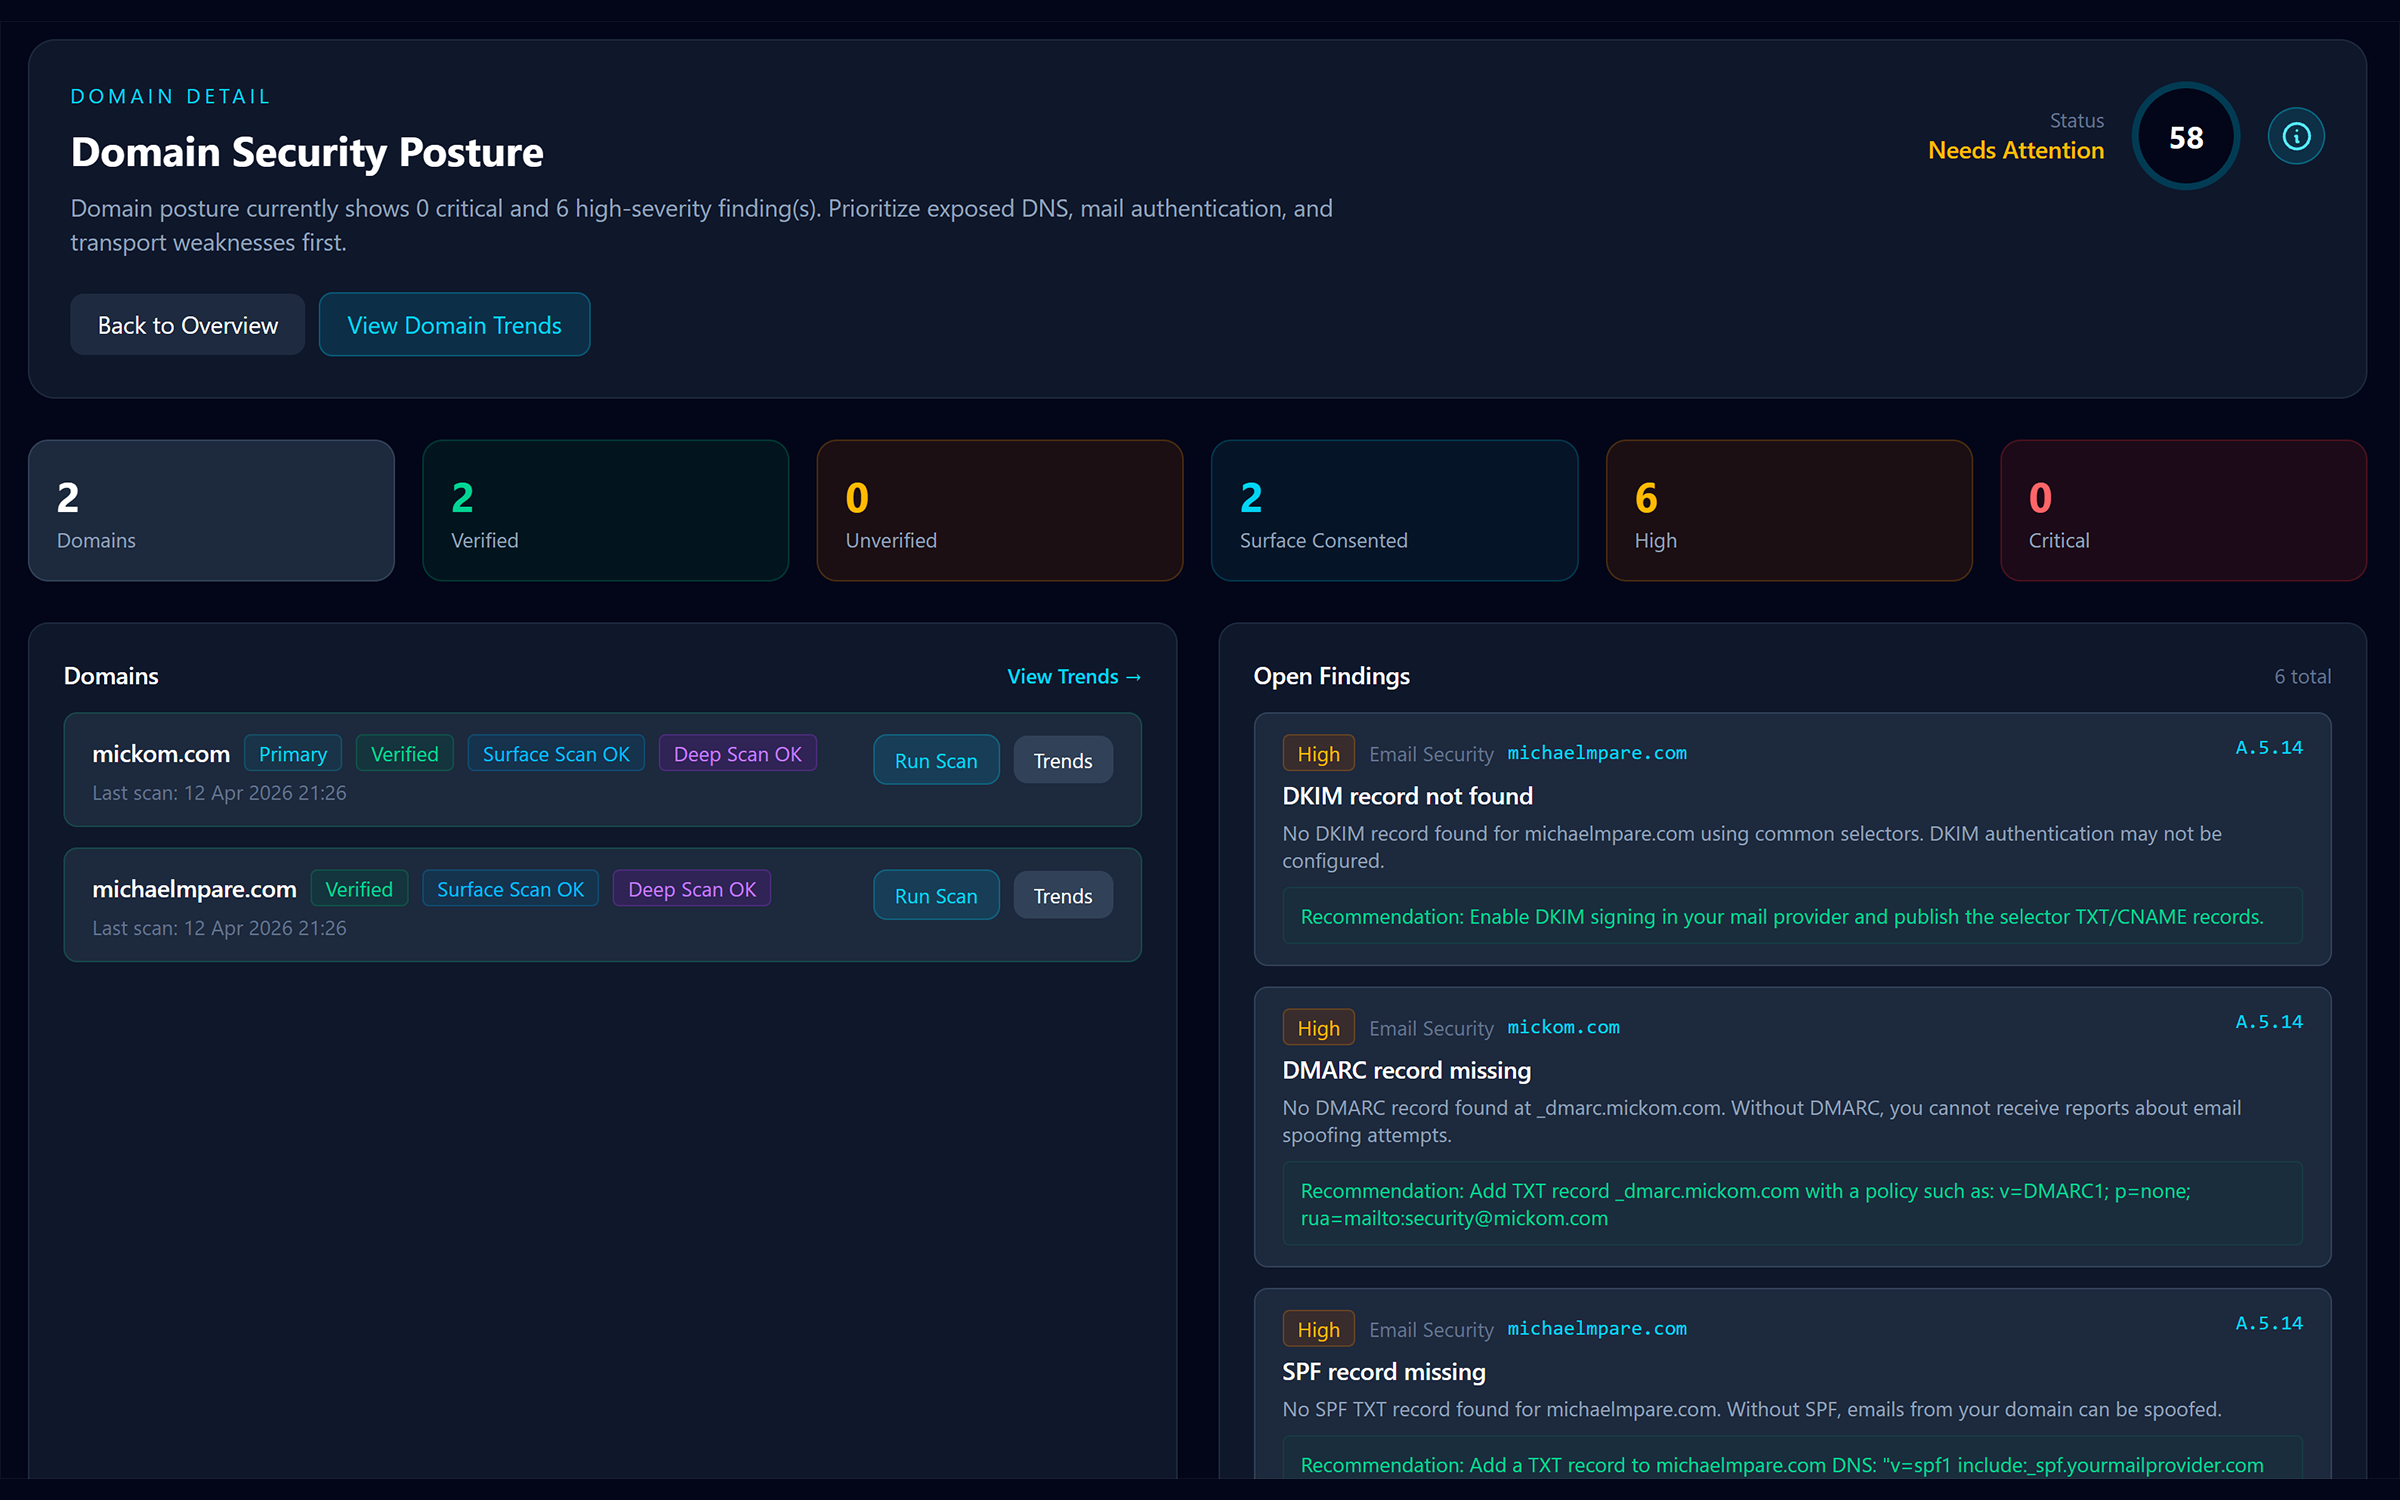
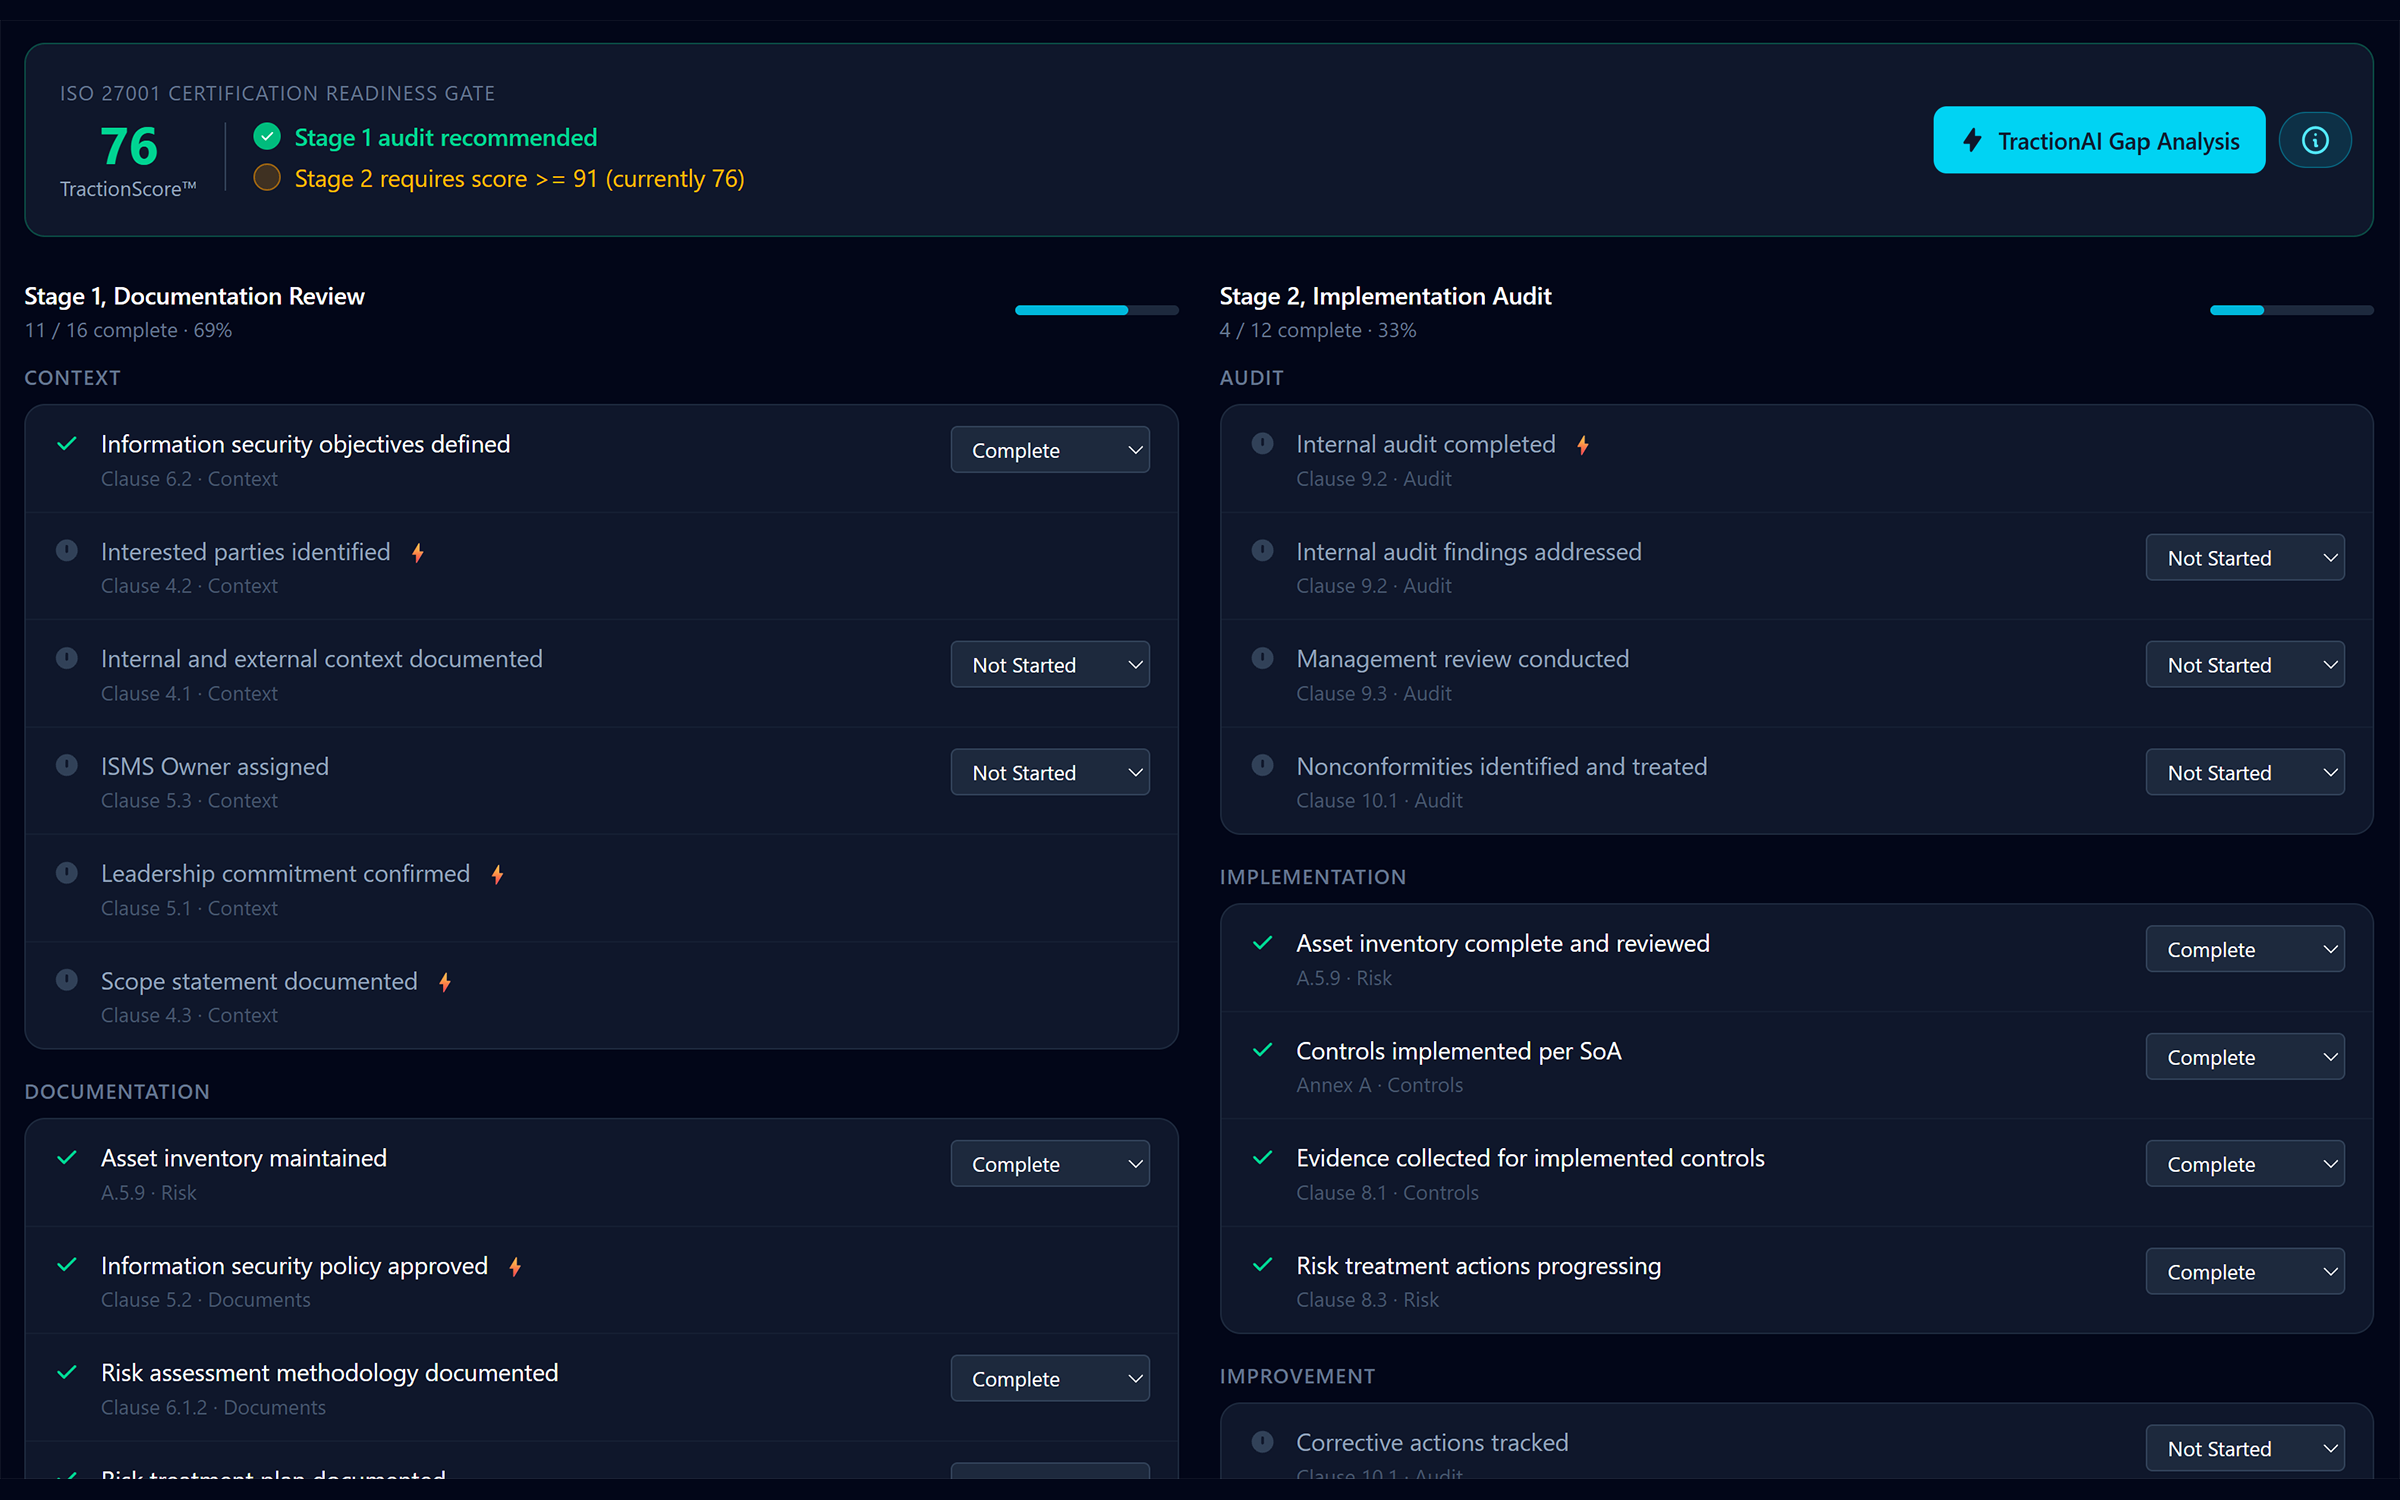
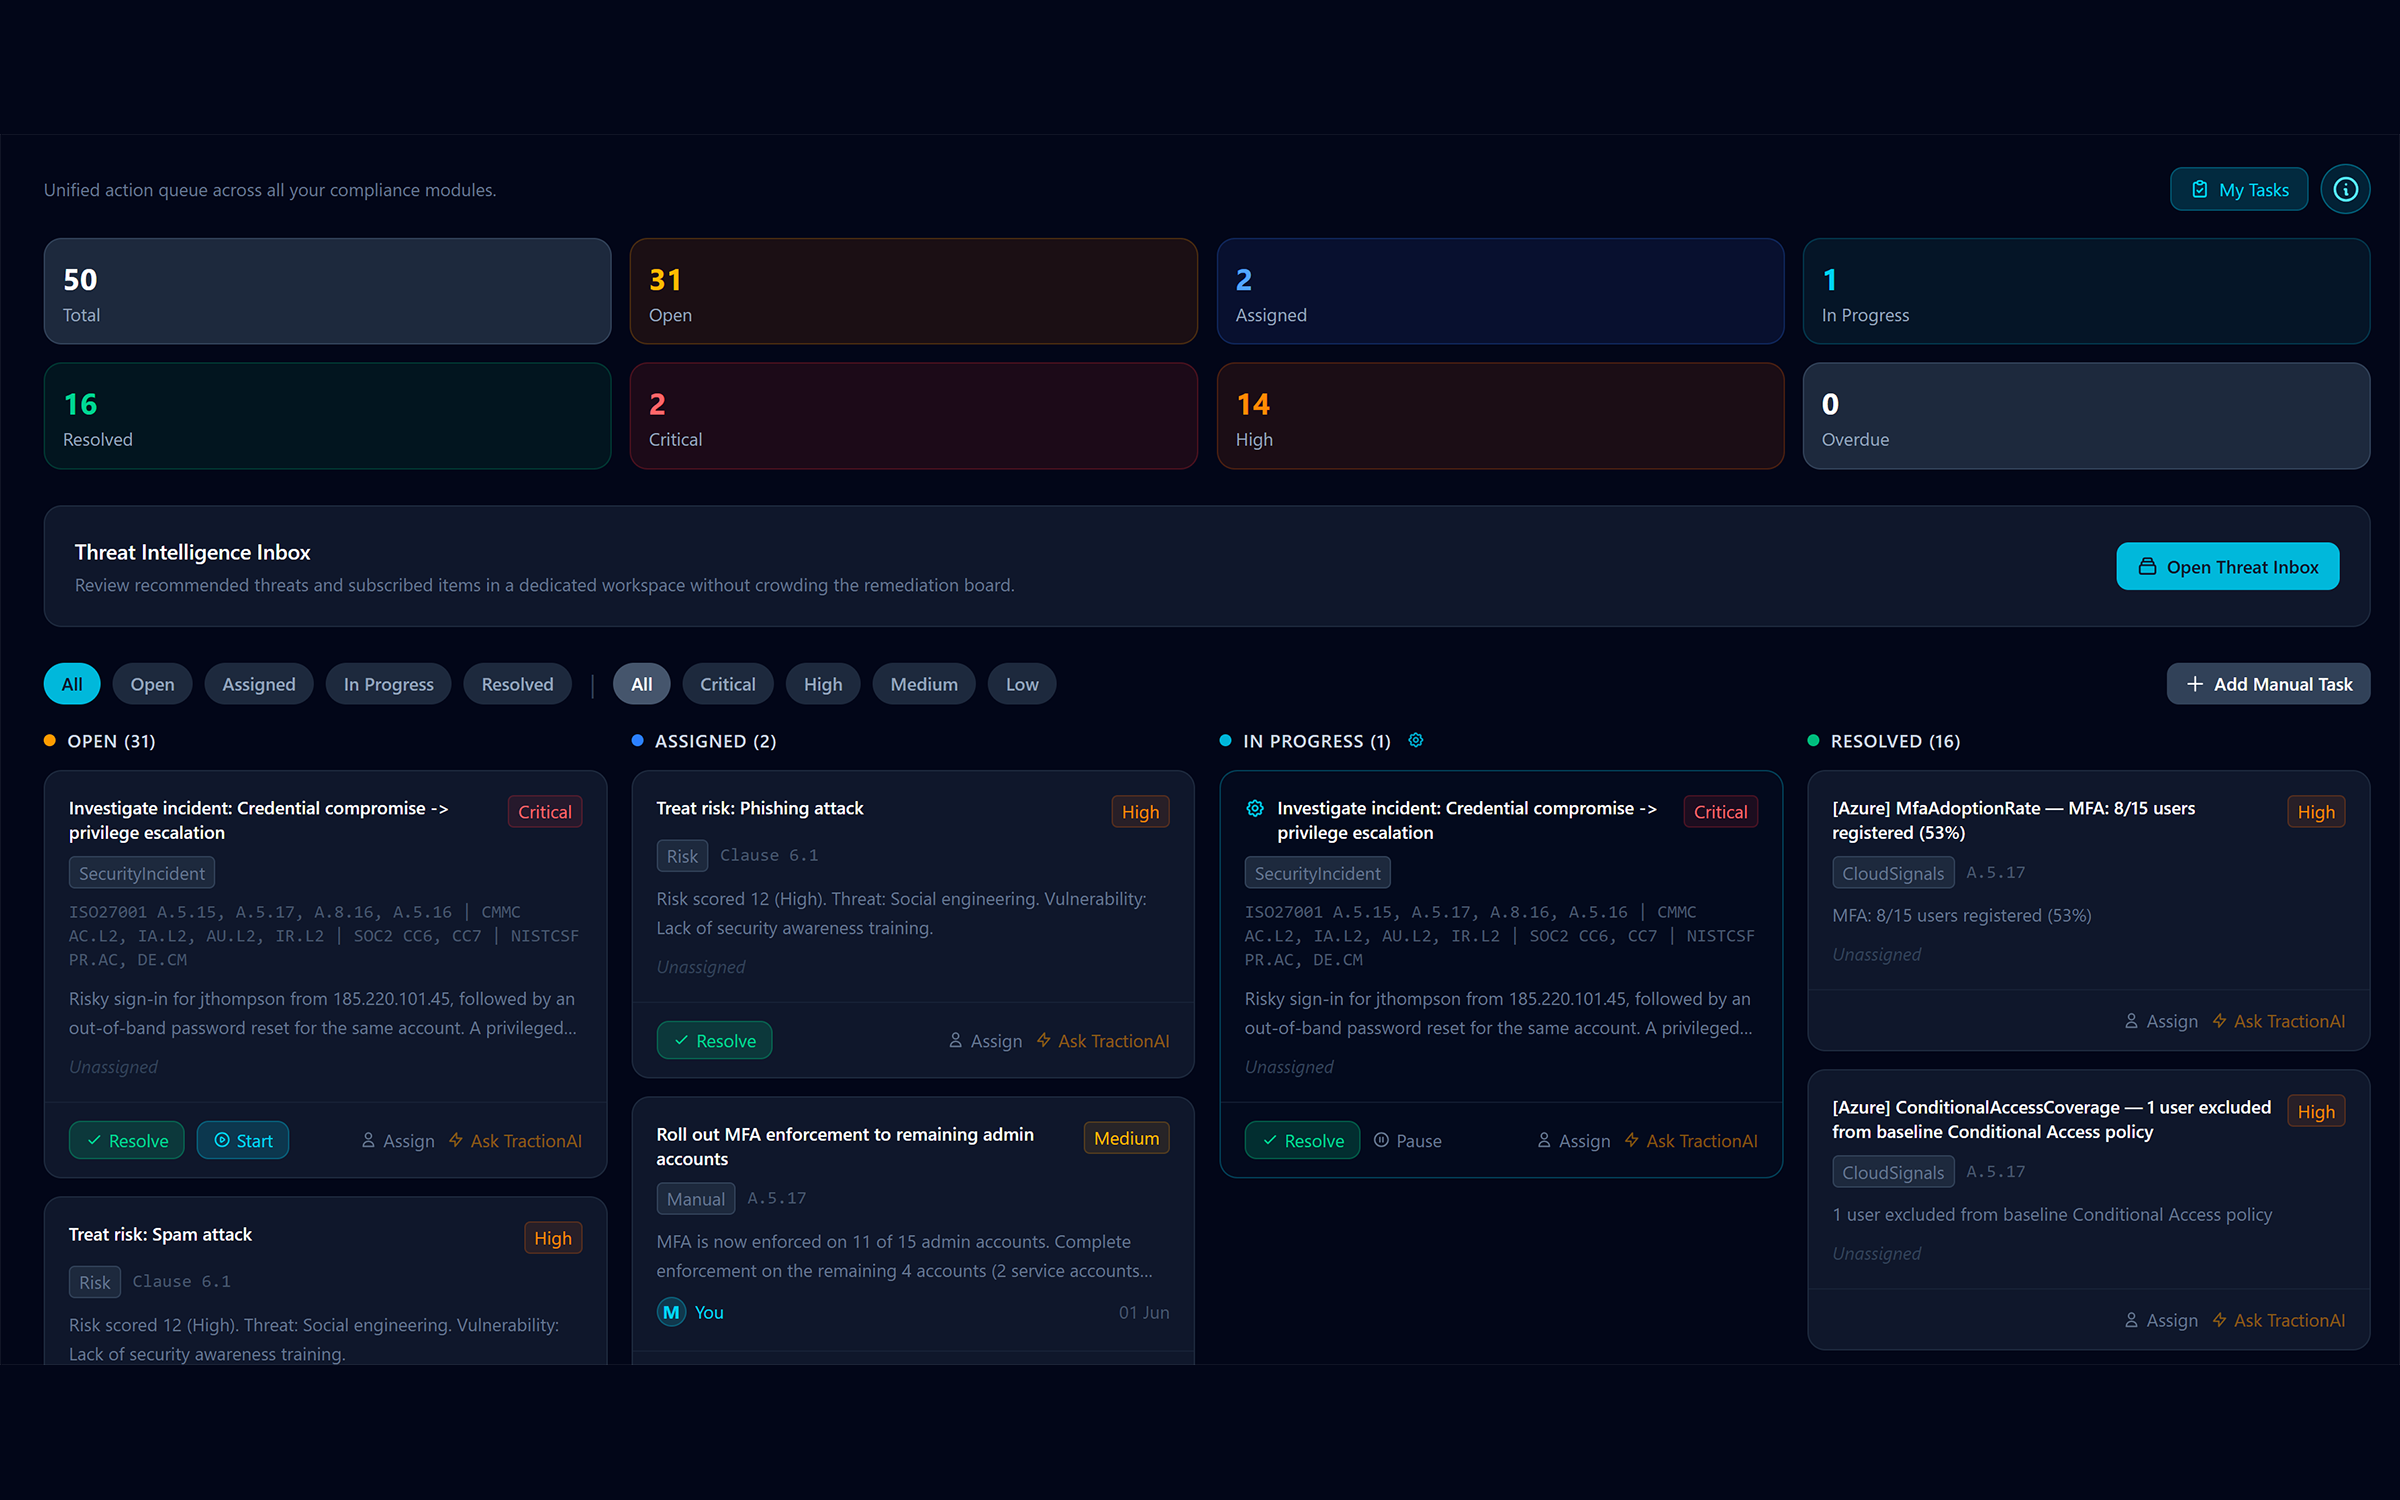
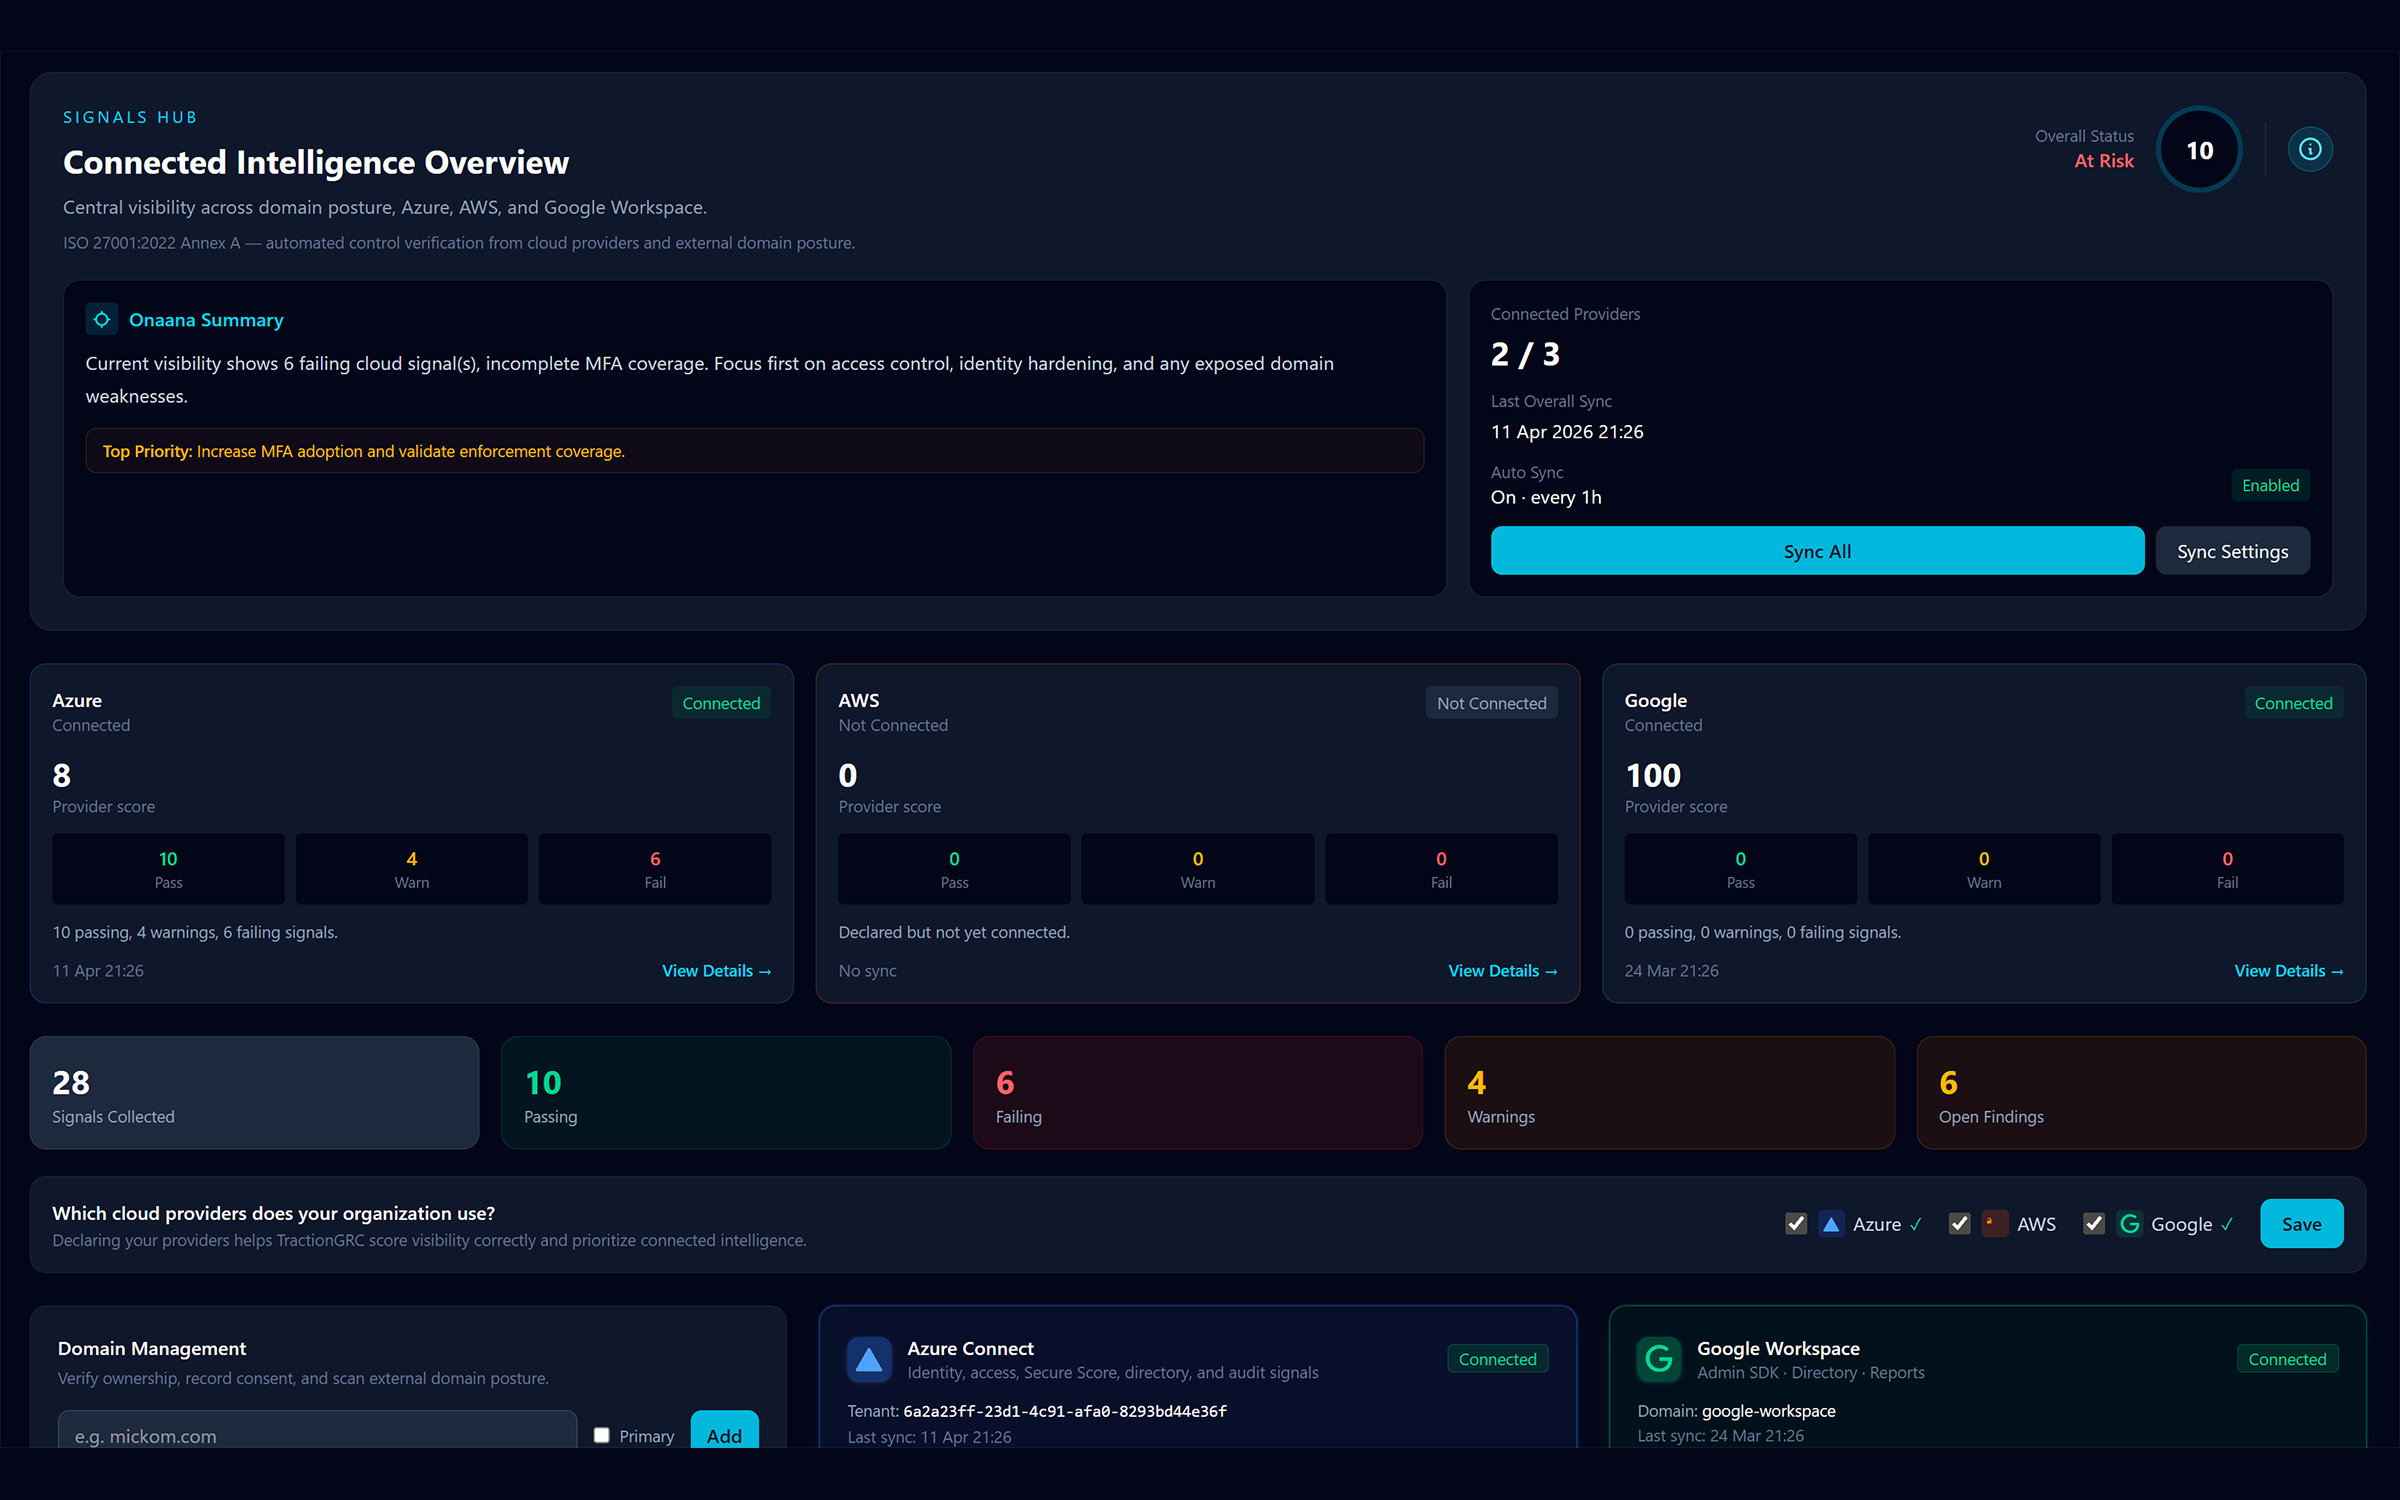
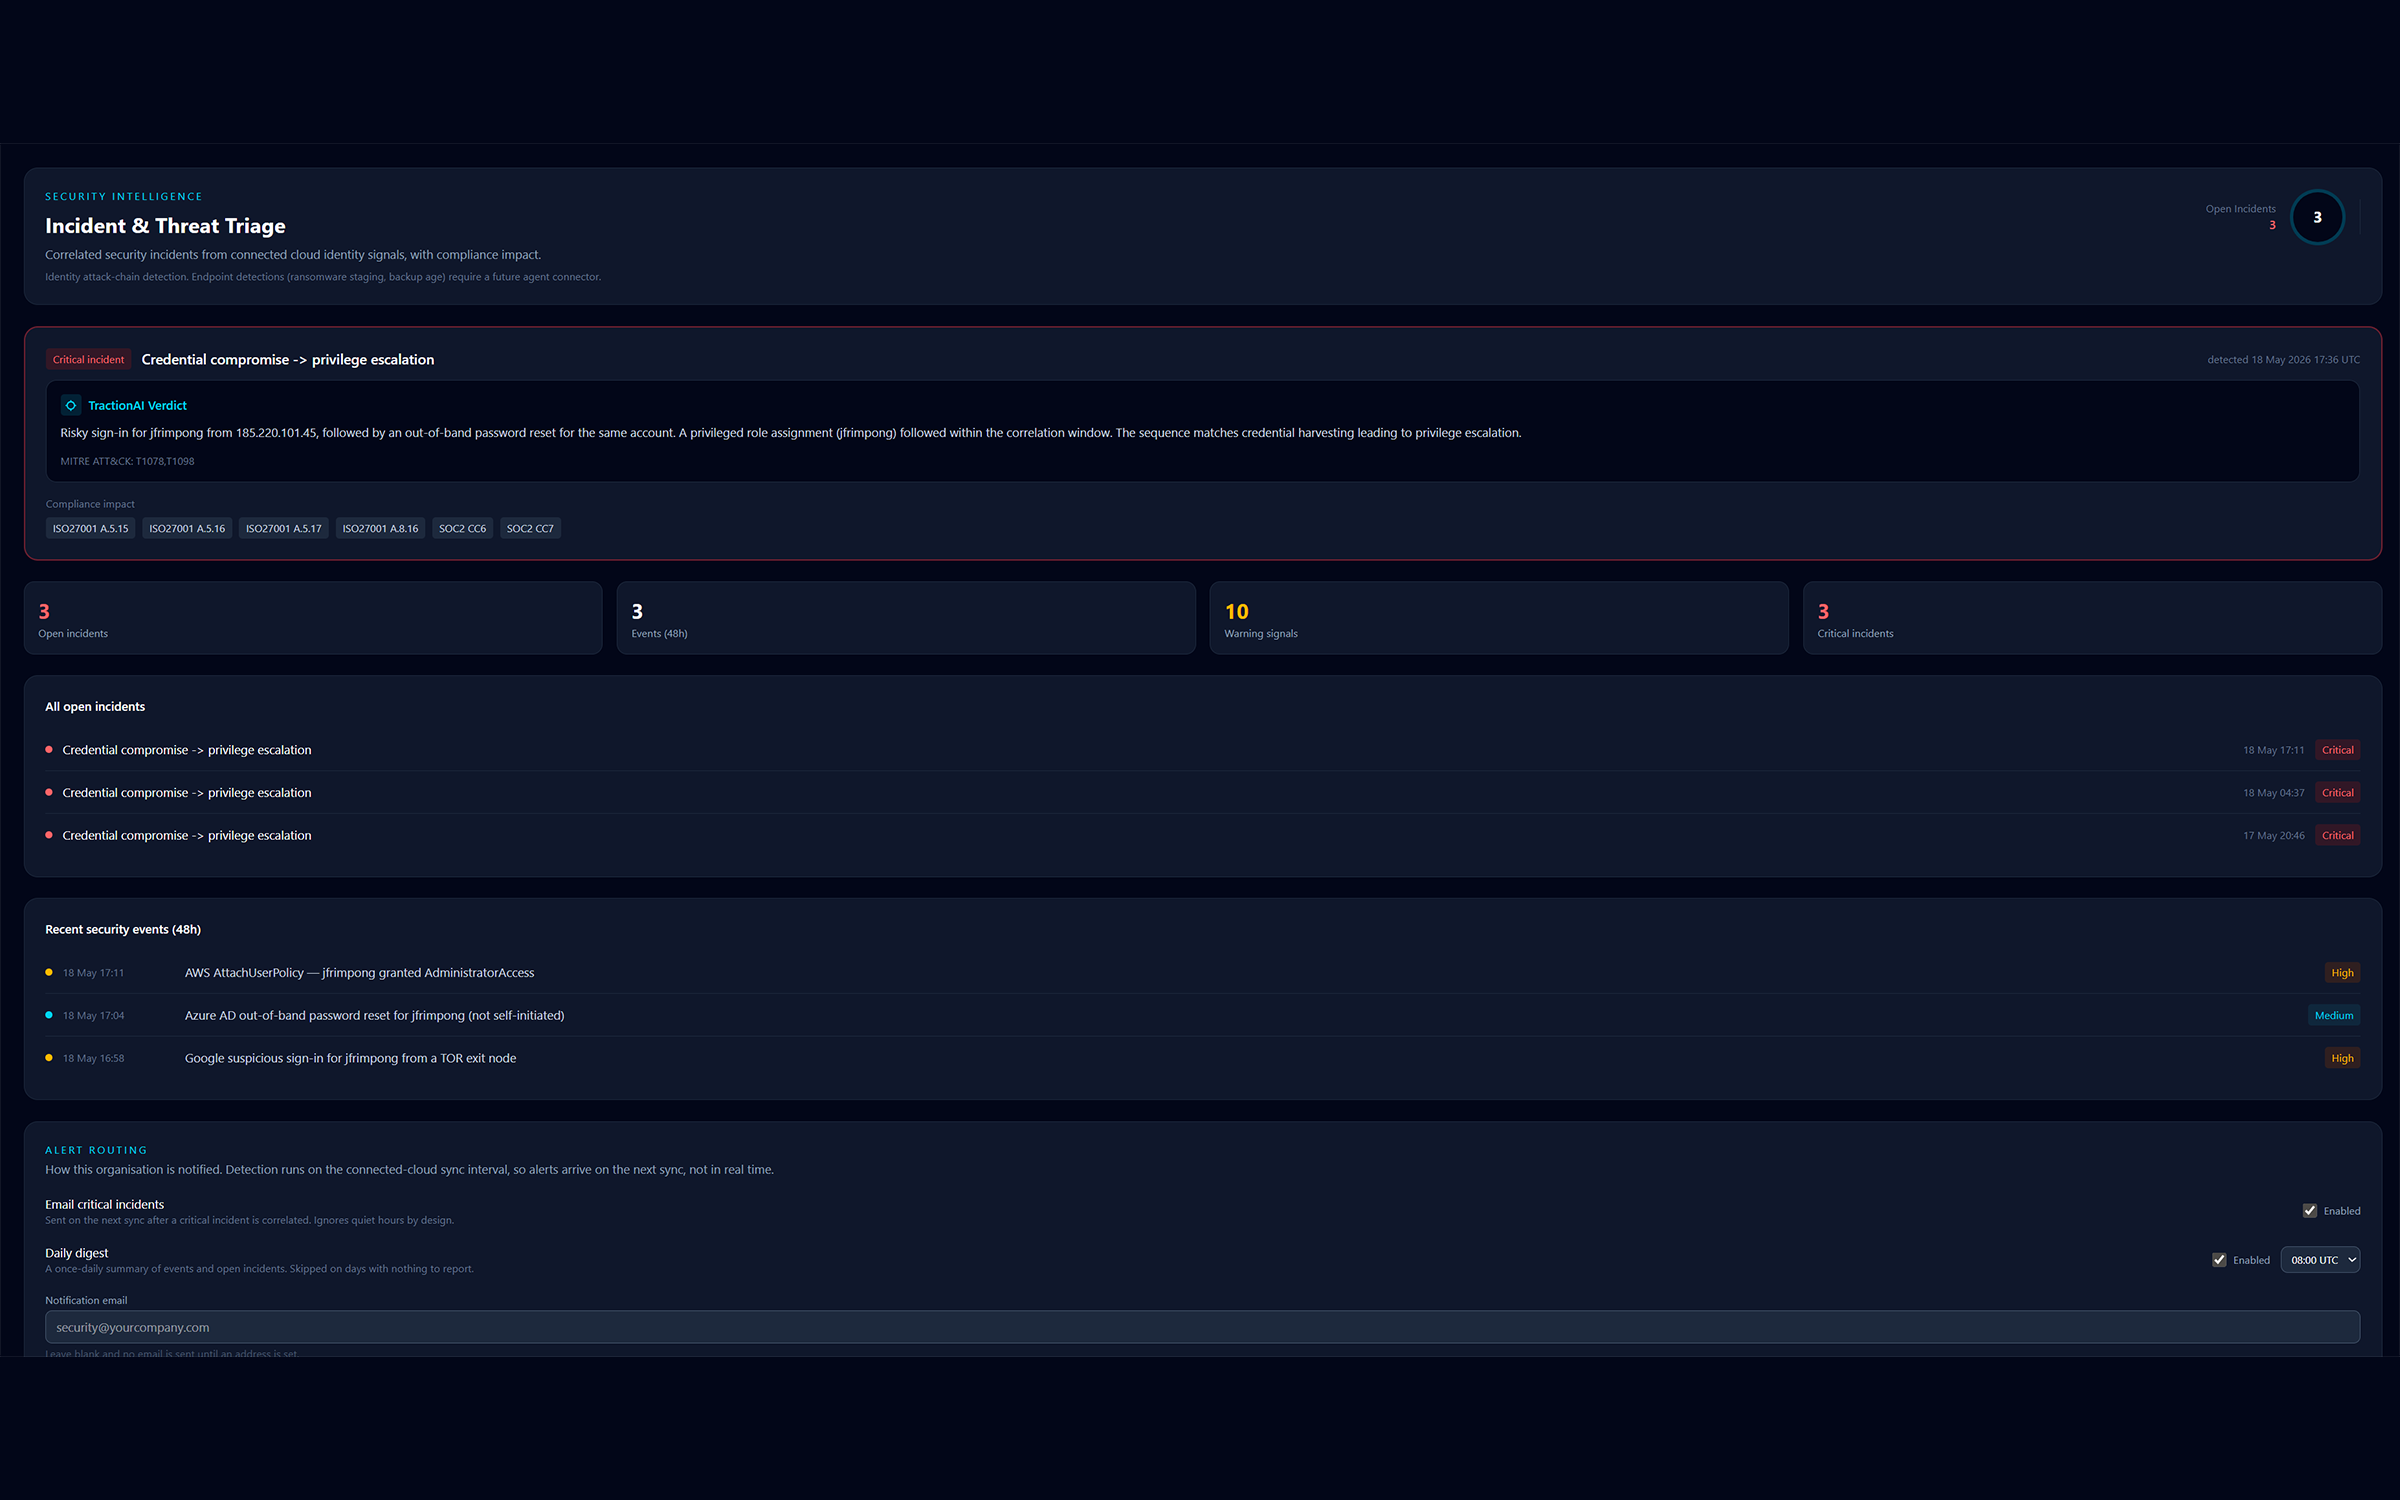
Ten views from a real Acme Demo Co tenant, mid-program, four months from Stage 1 audit. Click any slide to advance, or use the arrow keys.
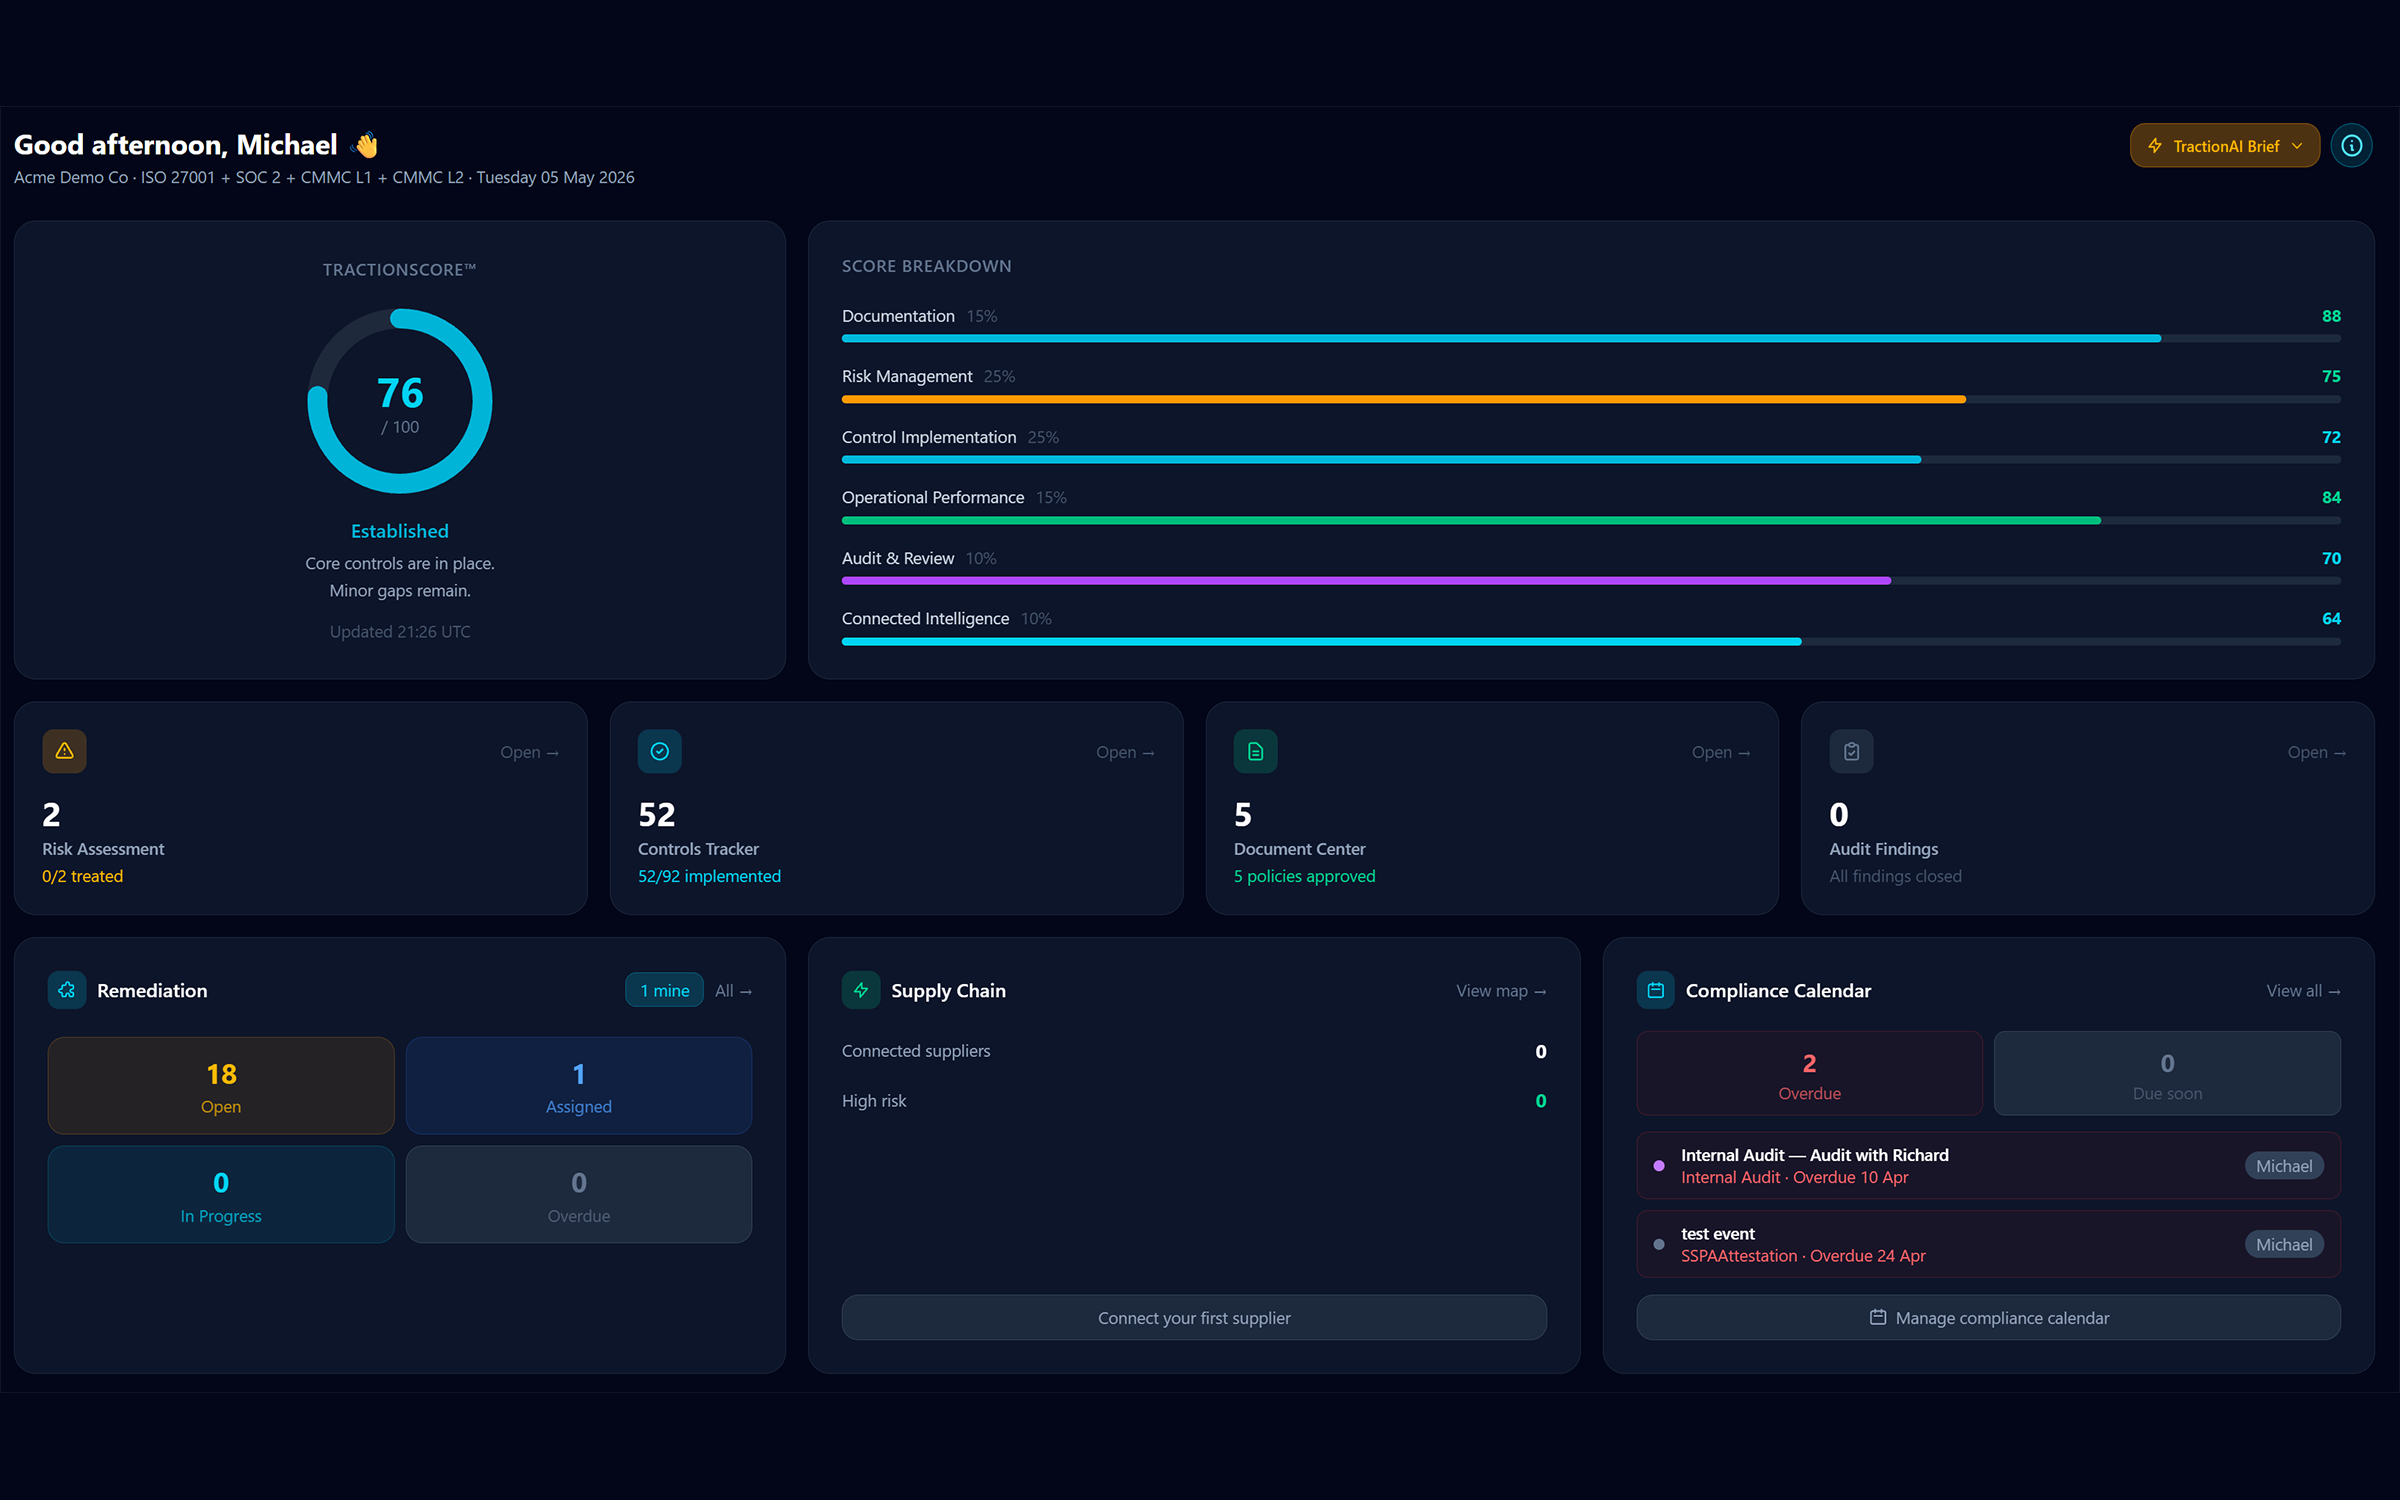
Dashboard
One score for your security program
TractionScore weighs six dimensions of ISMS health, so you see where you stand and what's drifting.

What makes the platform different
Three things that work together here
A checklist tells you what to do. These three show where you stand, do the first draft, and carry your evidence to the people who ask for it.
A shared signal for your security program
Six dimensions of ISMS health, weighted toward what auditors sample most, with live signals from your connected clouds. Customers, auditors, and leadership all see the same number.
See how it works →Drafts the things you've been putting off
Policies aligned to ISO 27001 Annex A clauses and your tech stack. Risk register entries with suggested likelihood and impact. Internal audit checklists, management review packs, questionnaire responses. Your team reviews and approves.
See how it works →Respond and issue from one workflow
Answer programs your customers send you on any plan. Prepare external questionnaires, such as Microsoft's SSPA, from Starter, with evidence you answer once and reuse. Issue your own from Professional.
Explore Supplier Assurance →Built for both
Whether you're winning business or governing risk
The work looks different at 10 people than at 500. The platform handles both, without forcing one team into the other team's setup.
Win the security conversation, not just the deal
Smaller teams lose deals not because their security is bad, but because they cannot prove it fast enough. The platform gives you the structure and the docs to back it up.
- Typical first ISO 27001 readiness: three to six months
- CMMC 2.0 Level 1 on Starter, Level 2 readiness on Professional
- Prepare SSPA and other external questionnaires from Starter
- TractionScore shows where you stand without paying for an audit
Run the program at scale, without losing the thread
At a certain size, the bottleneck is not effort. It is coordination. TractionGRC gives you a single source of truth that survives staff turnover and audit churn.
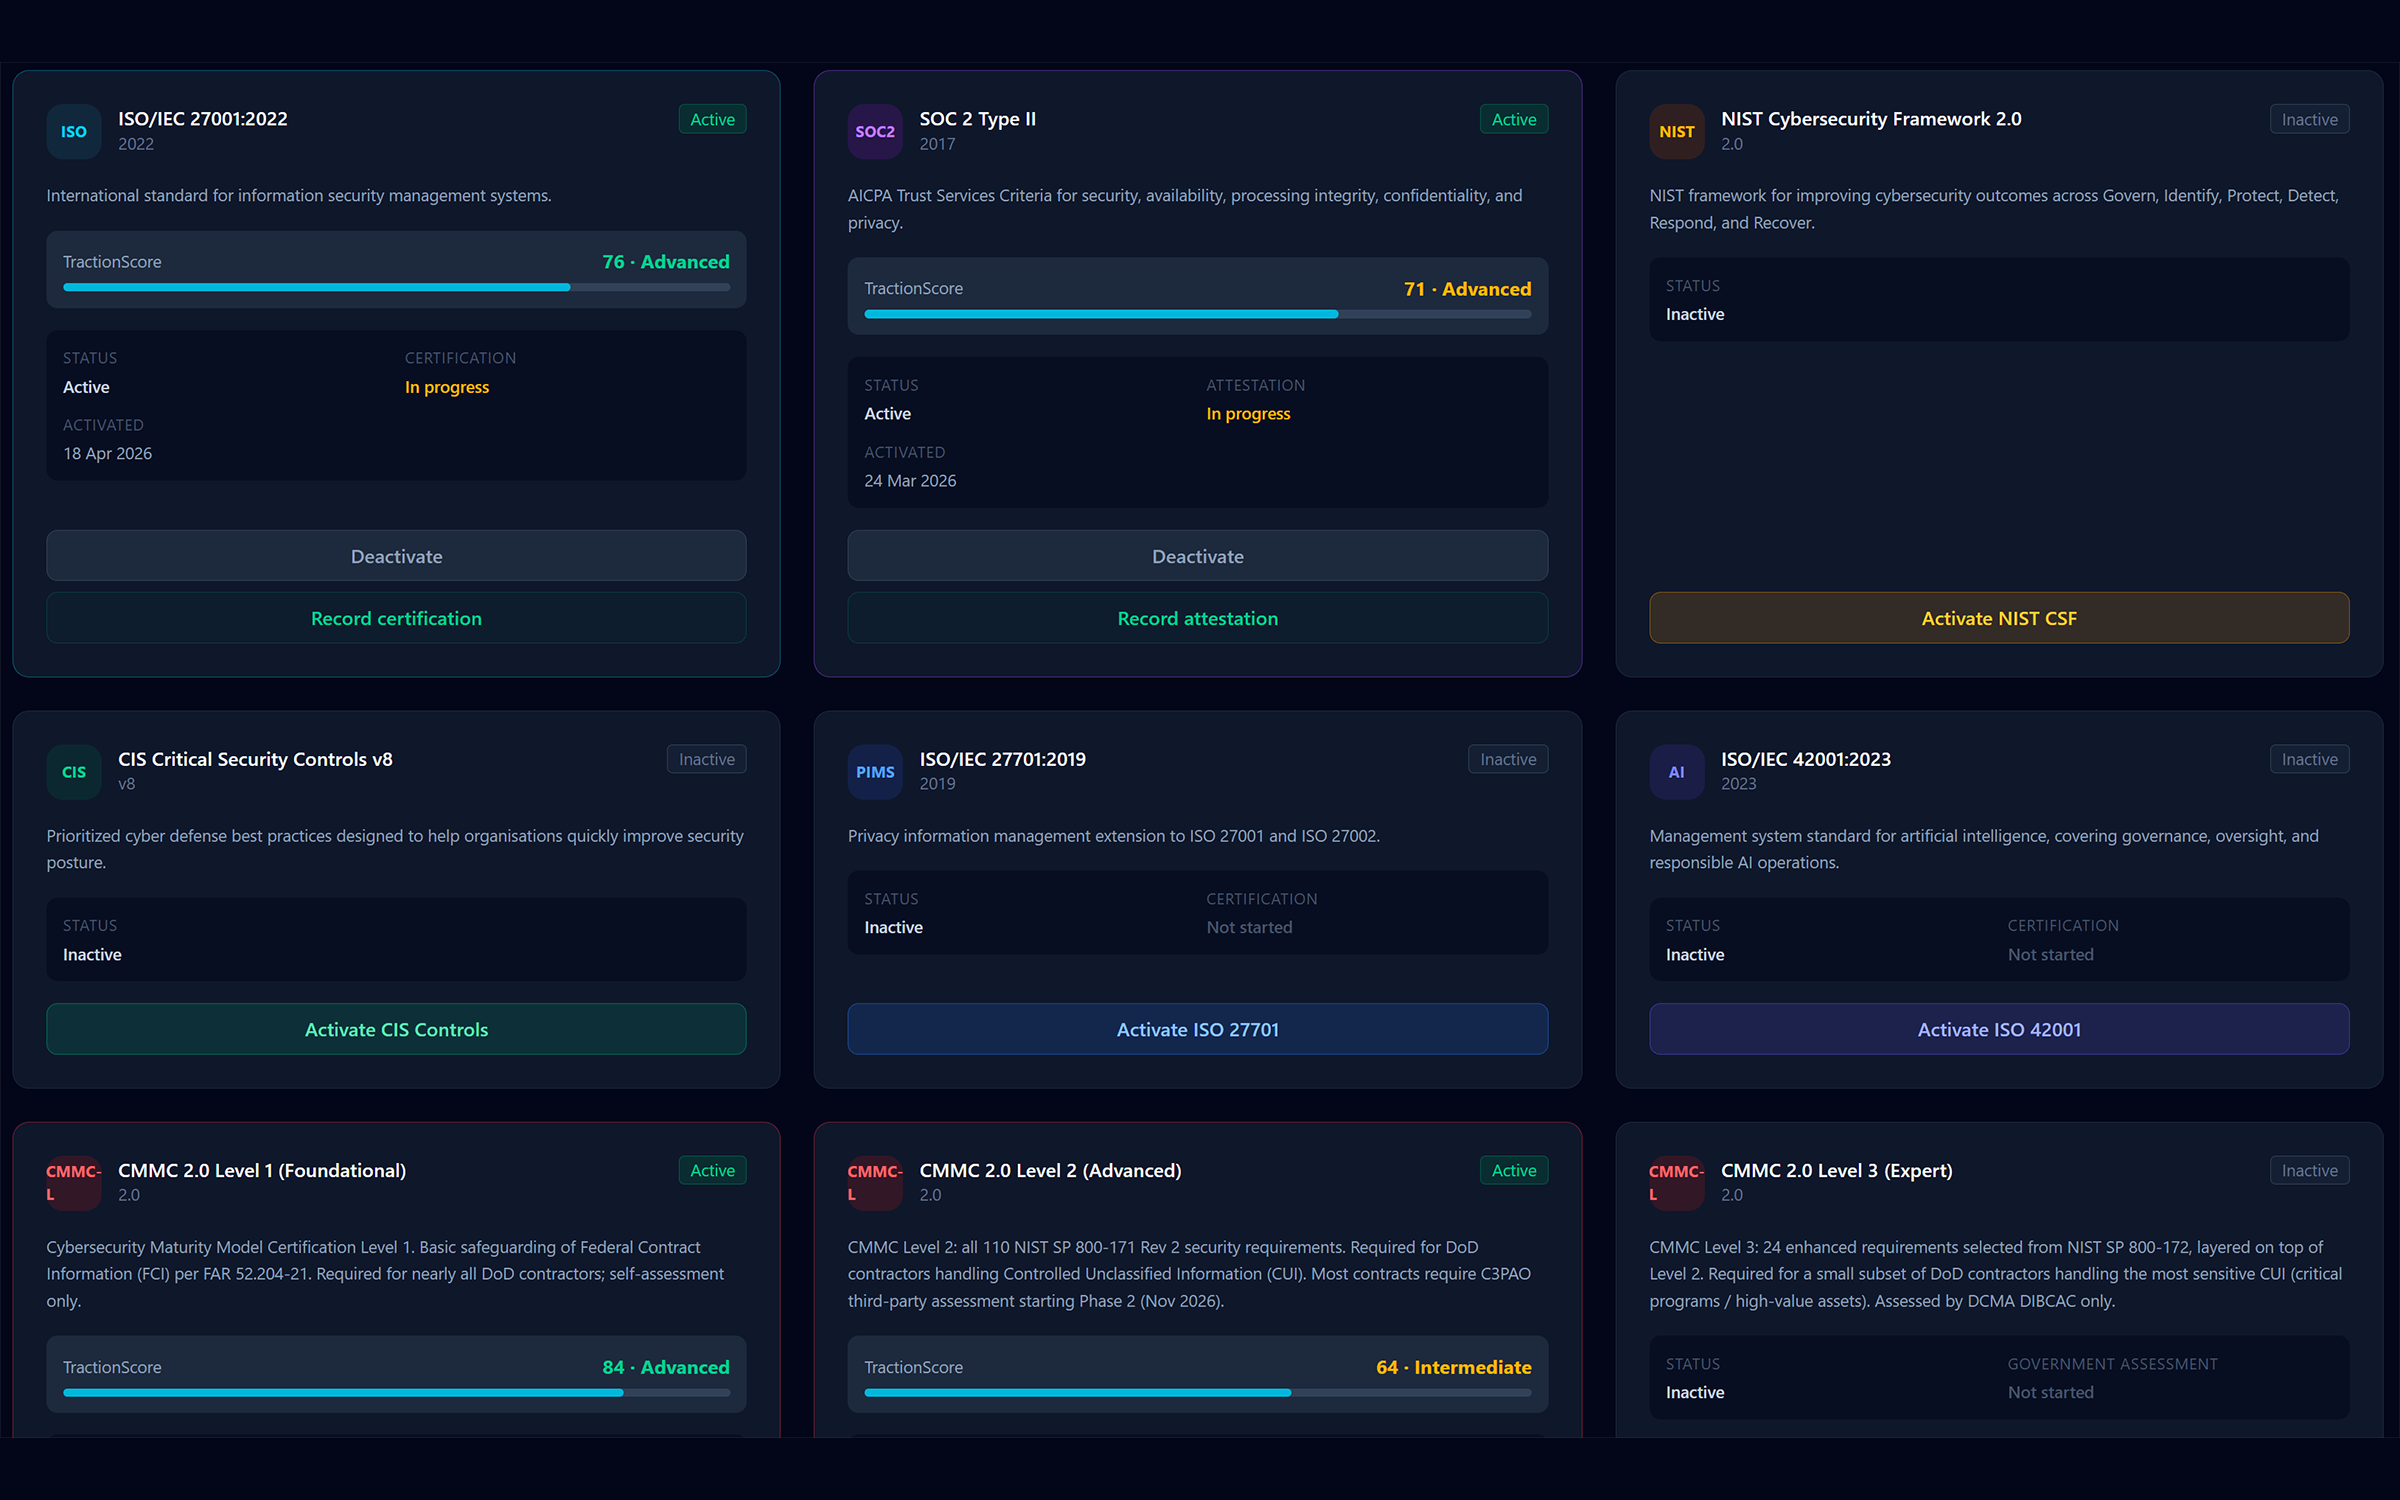
- Cross-mapped controls across ISO 27001, SOC 2, NIST CSF, ISO 42001, CMMC 2.0
- Issue SSPA and starter questionnaires to your supplier base
- Multiple subsidiaries from a single login, with per-org scoring
- Audit evidence linked to each clause and control
Framework coverage
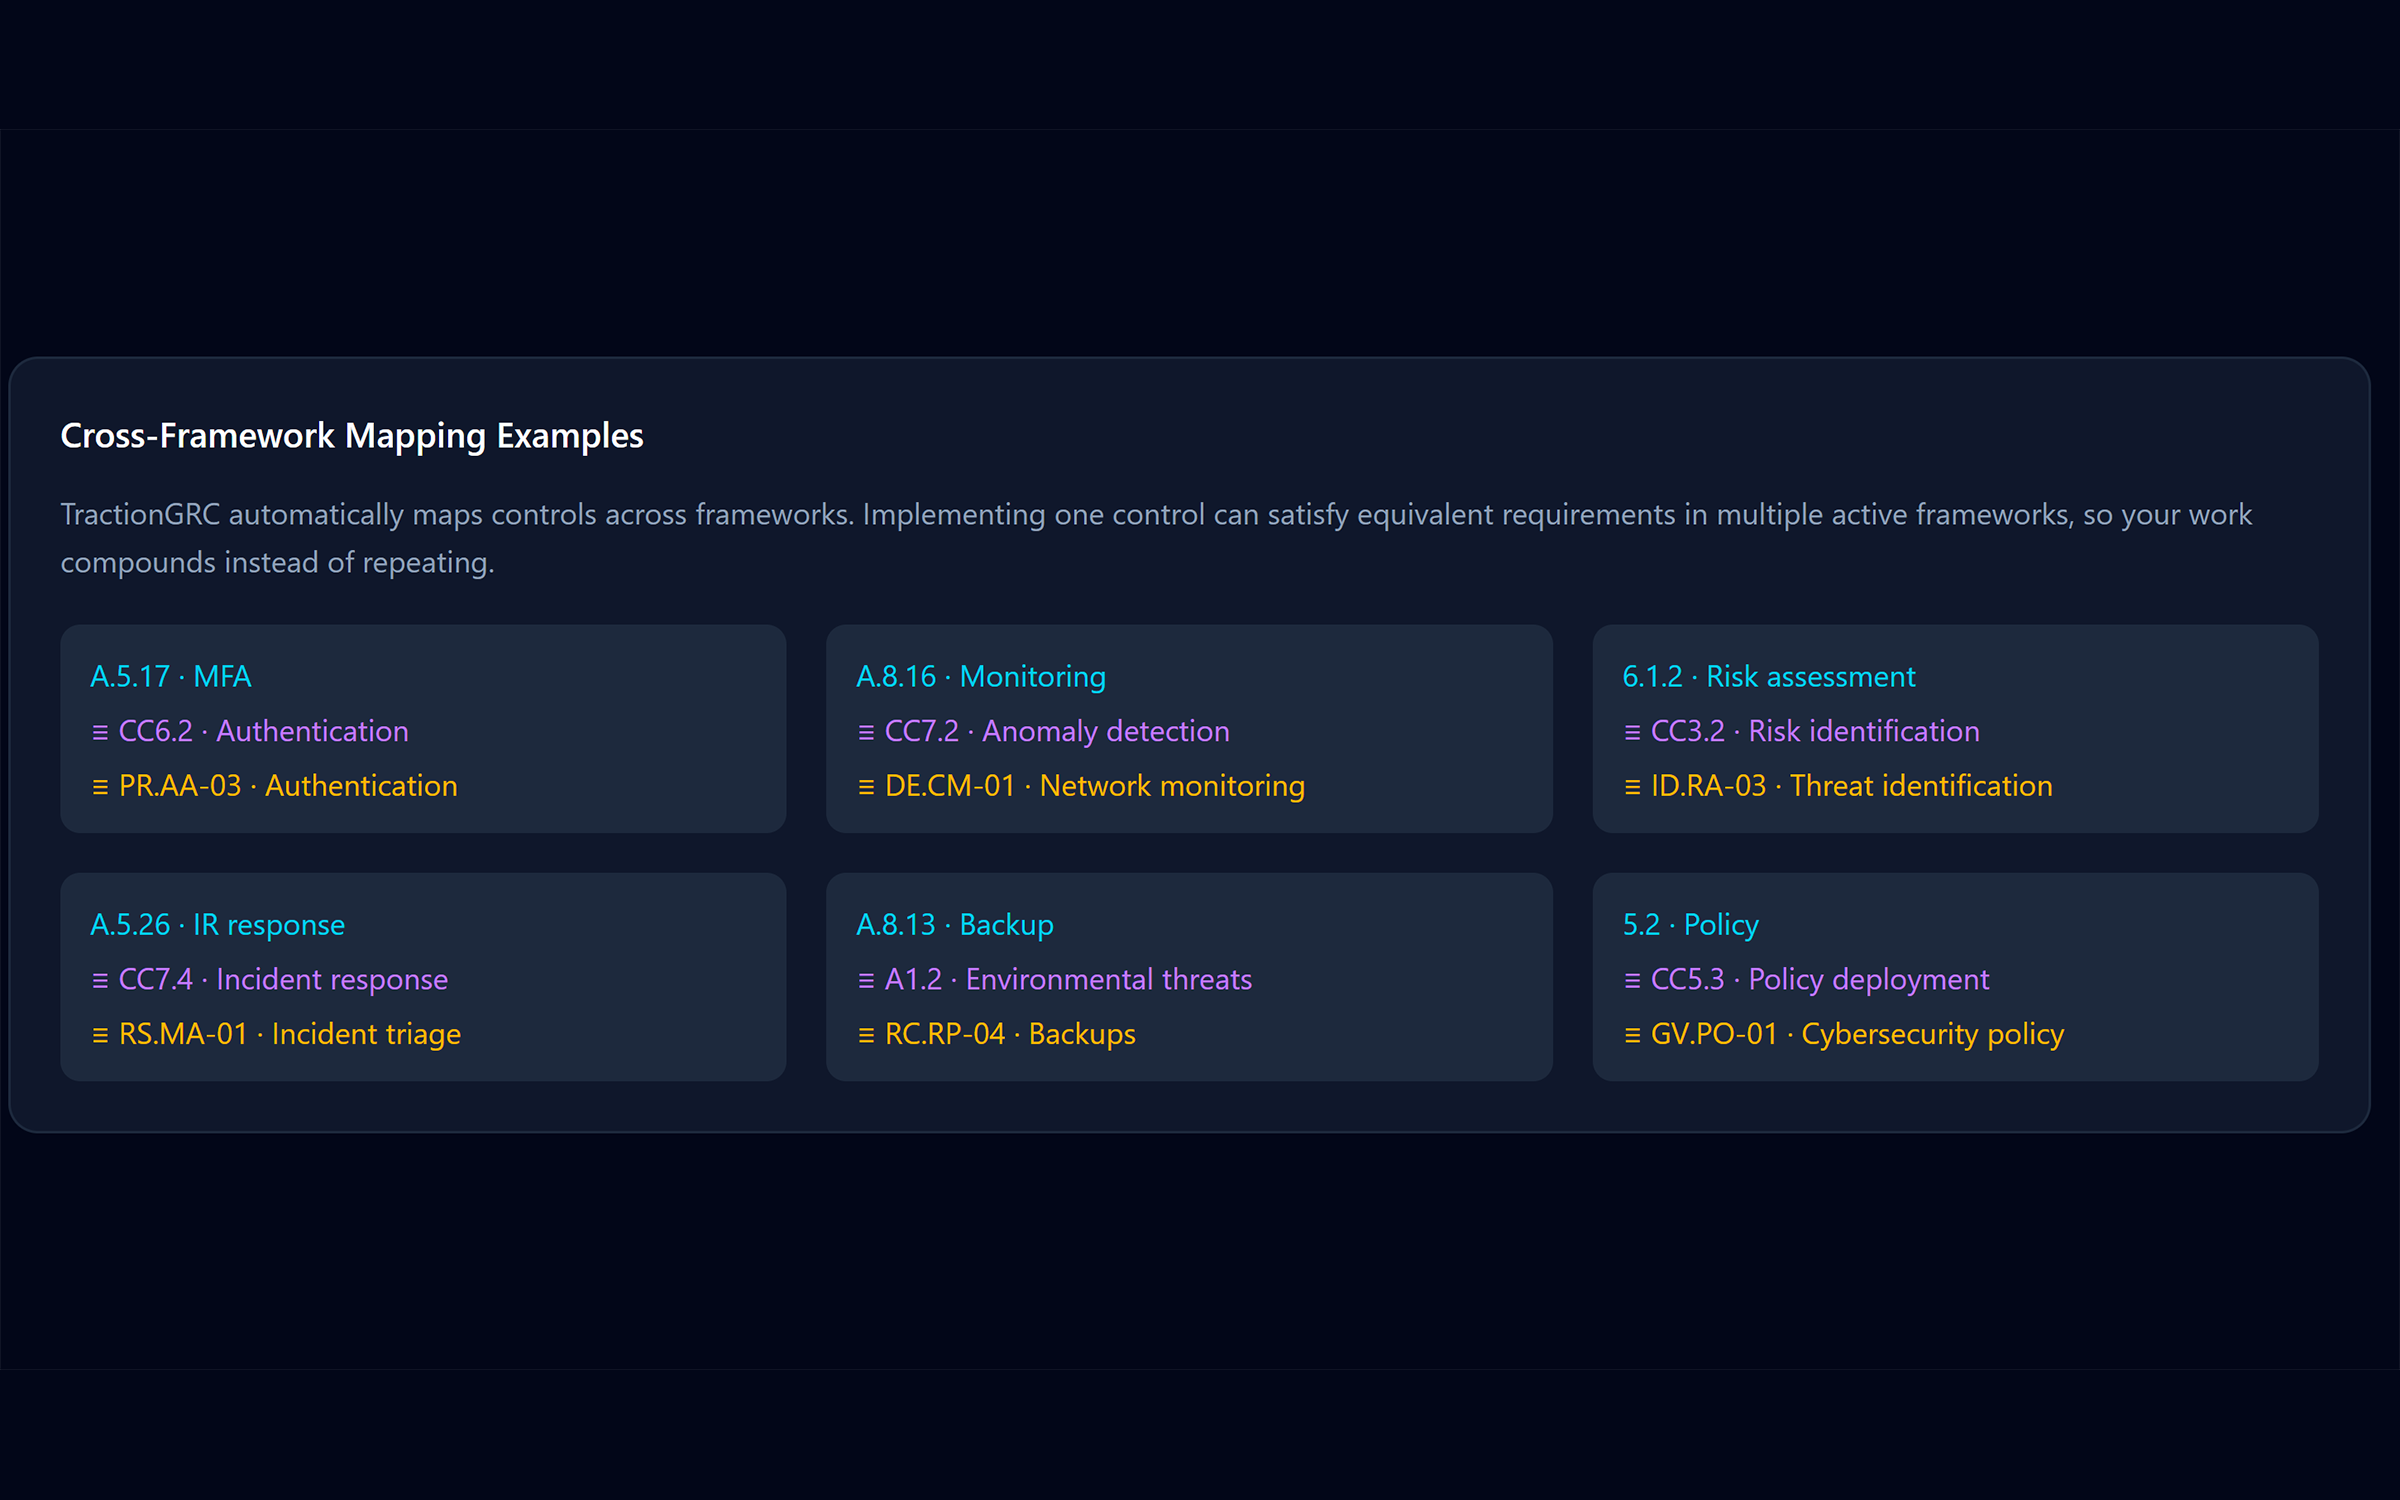
Cross-mapped, not copy-pasted
Implement a control once and it counts toward every framework it satisfies. MFA, for example, counts for NIST CSF PR.AA-03 and CMMC IA.L2-3.5.3 at the same time.
Pick a starting point
Start free and walk through Phase 1 in your first week. Or book 30 minutes with someone who has run a few of these programs. Either path, no pressure.
Quick assessment
Get tailored recommendations
Five quick questions. About 30 seconds. We'll show you what we recommend before asking for anything in return.
Here's what we recommend
Want this sent to you?
Our team follows up within 24 hours either way. Untick the box below if you'd rather not get a copy by email. We won't add you to a marketing list.
Thanks. We'll be in touch.
We've sent your recommendations to and our team will follow up within 24 hours.
Our team will follow up at within 24 hours.