CMMC compliance software for small defense contractors
TractionGRC tracks all three CMMC levels against NIST SP 800-171 Rev 2 and shows your progress in one score. With Phase 2 suspended since July 2026, contracts accept Level 1 and Level 2 self-assessments, and DFARS 252.204-7012 still applies, so the work is the same: implement the 110 requirements and keep your evidence current.
Last checked: October 29, 2026
Where CMMC stands today
Last checked: October 29, 2026. We recheck this monthly.
| Item | Status |
|---|---|
| CMMC rule (32 CFR Part 170) | In effect since December 16, 2024. Not repealed. |
| Phase 1 | Began November 10, 2025: Level 1 and Level 2 self-assessments in new DoD contracts. |
| Phase 2 (C3PAO assessments) | Suspended on July 13, 2026 while DoD reviews the program. No restart date yet. |
| What solicitations accept now | Level 1 and Level 2 self-assessments (DFARS Class Deviation 2026-O0025, Revision 3, September 3, 2026). |
| CMMC clause in new contracts | Automatic for contracts involving FCI or CUI from November 10, 2028. |
| Still required today | DFARS 252.204-7012 and the 110 requirements of NIST SP 800-171 Rev 2, a current score in SPRS, annual affirmations, and 72-hour cyber incident reporting. |
| Flow-down | Applies to subcontractors that handle the same FCI or CUI (DFARS 252.204-7021). |
This is a summary, not legal advice. The requirement in each solicitation and contract is what applies to you.
Which level you need
Level 1
Federal Contract Information (FCI)
Requirements: 15 safeguarding requirements from FAR 52.204-21, assessed as 17 practices
Assessment: Annual self-assessment and affirmation in SPRS
In TractionGRC: Starter plan, $349 a month
Level 2
Controlled Unclassified Information (CUI)
Requirements: 110 requirements of NIST SP 800-171 Rev 2
Assessment: Self-assessment while Phase 2 is suspended; C3PAO assessment where a contract requires it once Phase 2 resumes
In TractionGRC: Professional plan, $999 a month
Level 3
CUI on critical, high-value programs
Requirements: 24 requirements from NIST SP 800-172, on top of Level 2
Assessment: Government-led assessment by DCMA DIBCAC
In TractionGRC: Enterprise plan, priced per customer
Your solicitation names the level. If you only receive FCI, such as contract terms and invoices, you need Level 1. If you receive CUI, such as controlled technical drawings or specifications, you need Level 2.
What TractionGRC does for CMMC
Every practice, with an owner and evidence
The Level 1, 2 and 3 libraries list each practice and requirement. Assign an owner, set the implementation status, and attach evidence, so your self-assessment rests on records rather than memory.
ISO 27001 work counts toward CMMC
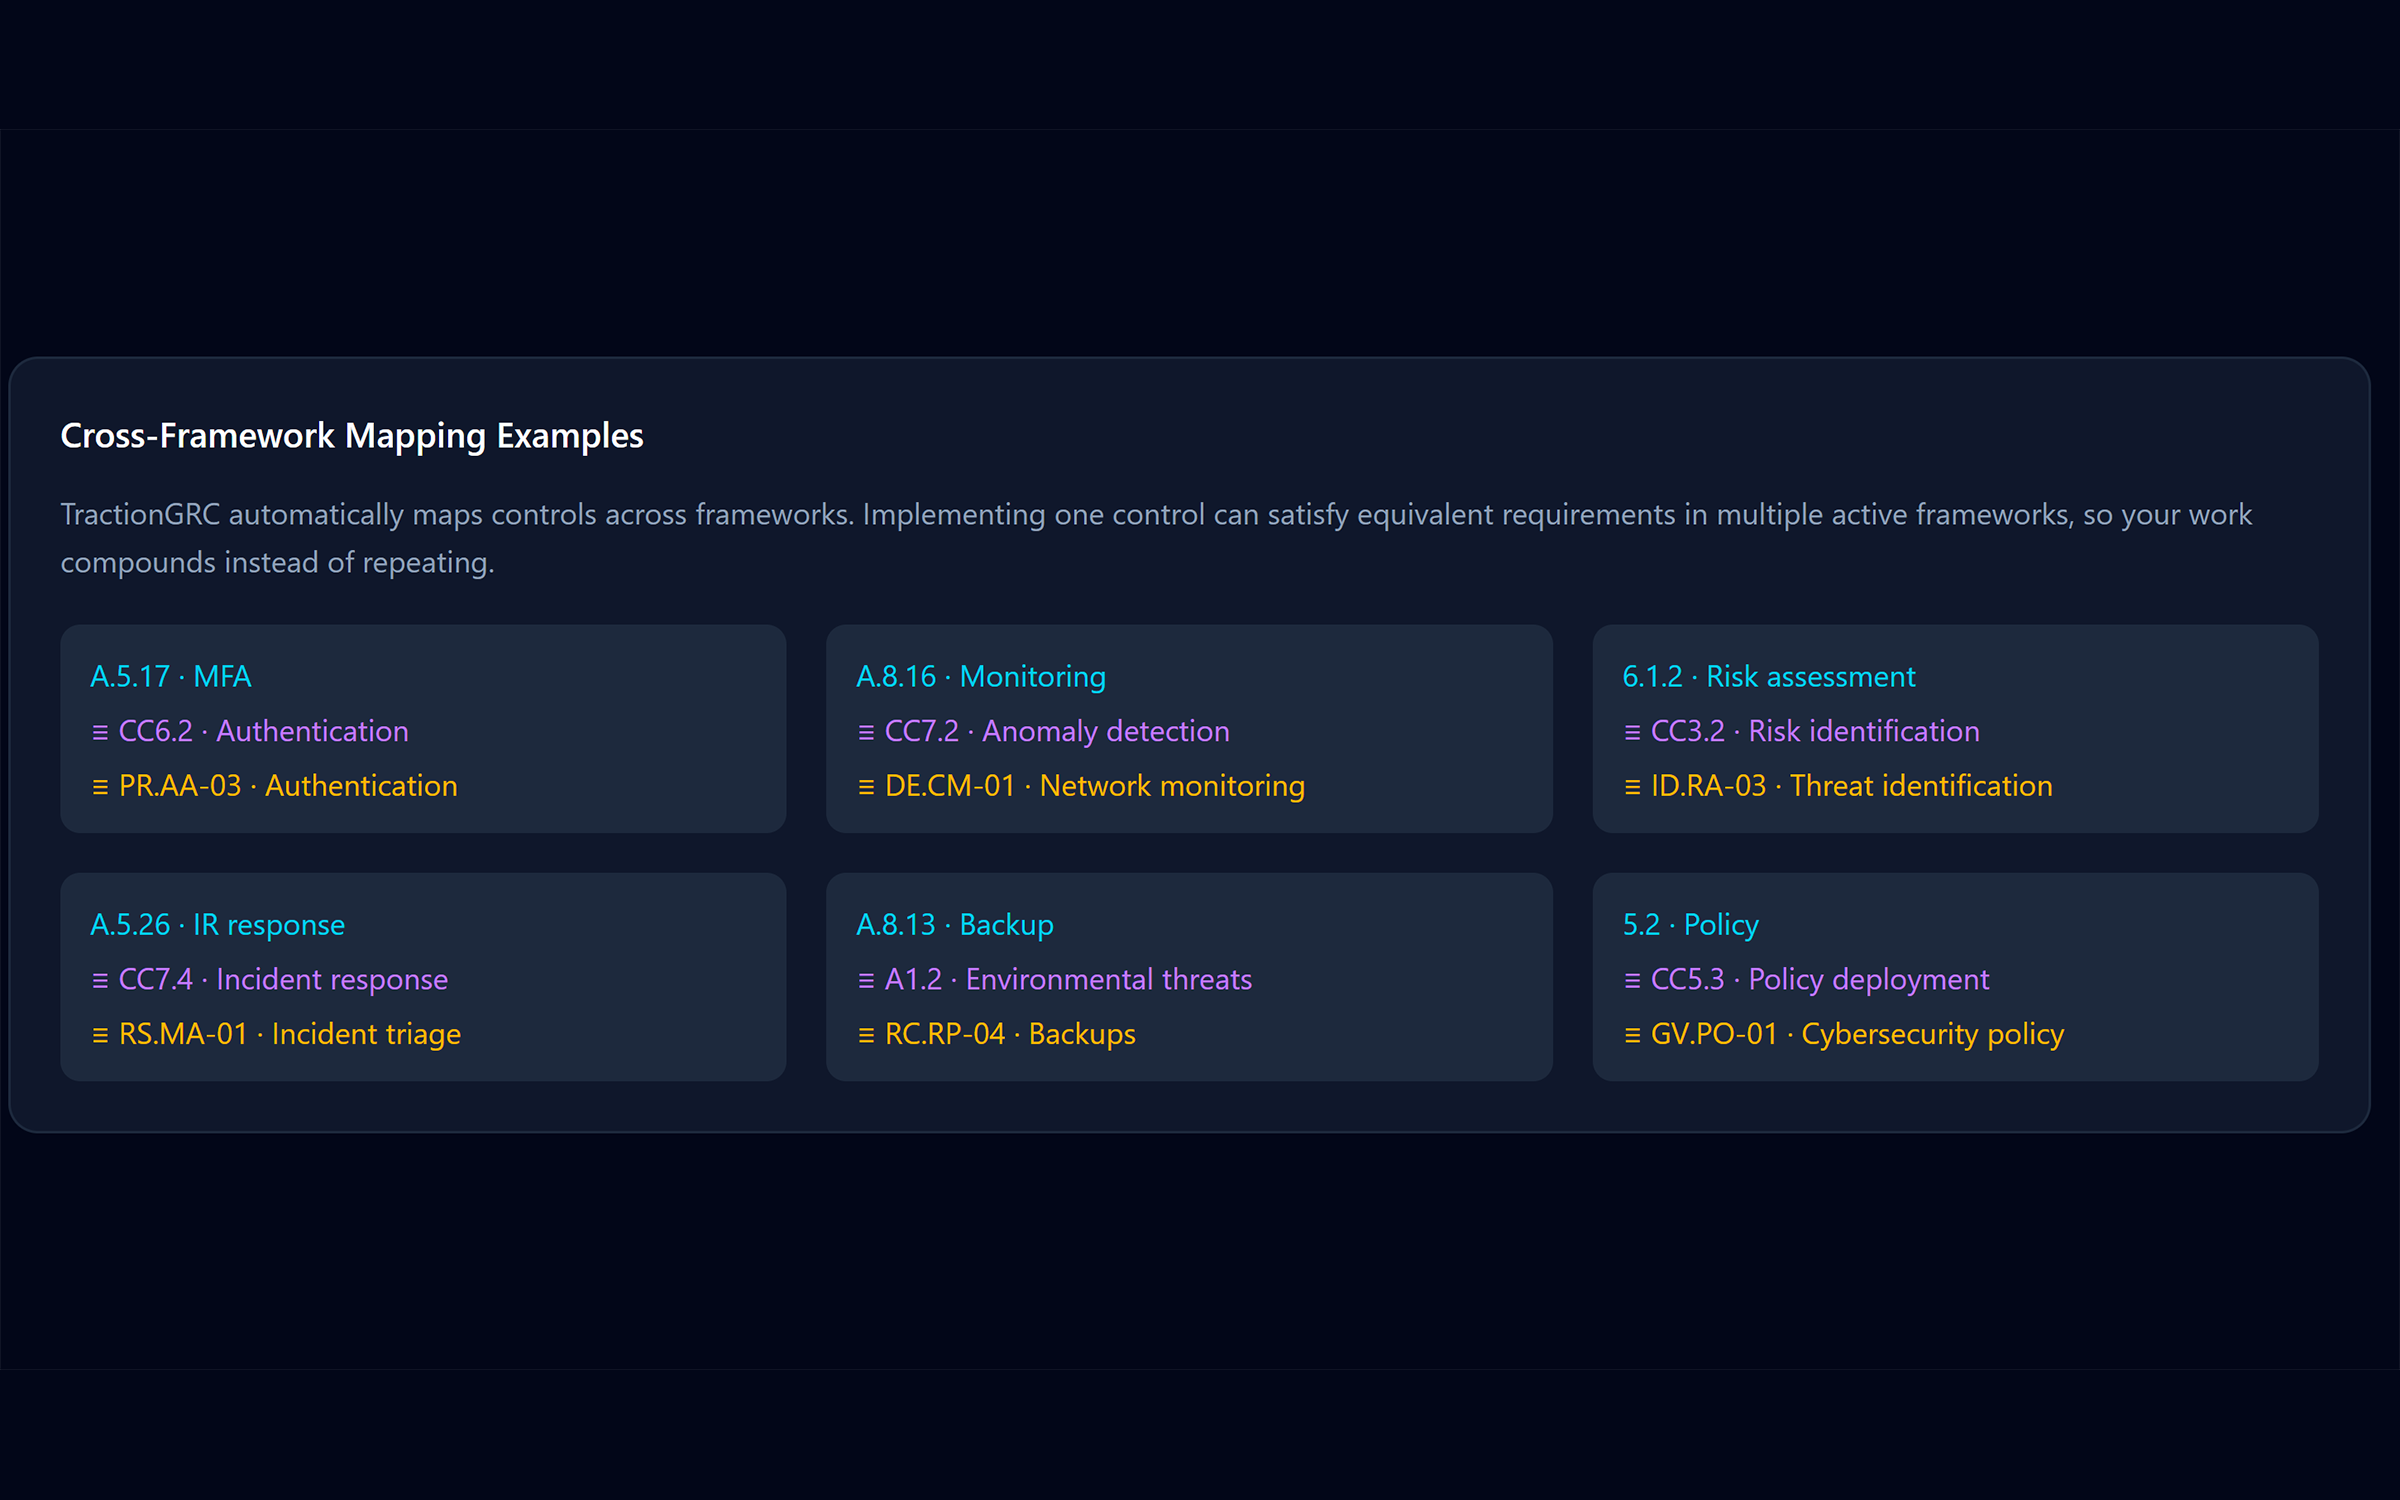
Every CMMC requirement, at all three levels, is mapped to its closest ISO 27001:2022 Annex A control. A control you implement once shows up against both.
Policies drafted by TractionAI
TractionAI drafts the 14 Level 2 policies, one for each NIST SP 800-171 family, for you to review, edit and approve, with versions and approvals tracked.
A readiness checklist for each level
See what is done and what is left, including scope, gap tracking and the SPRS affirmation step.
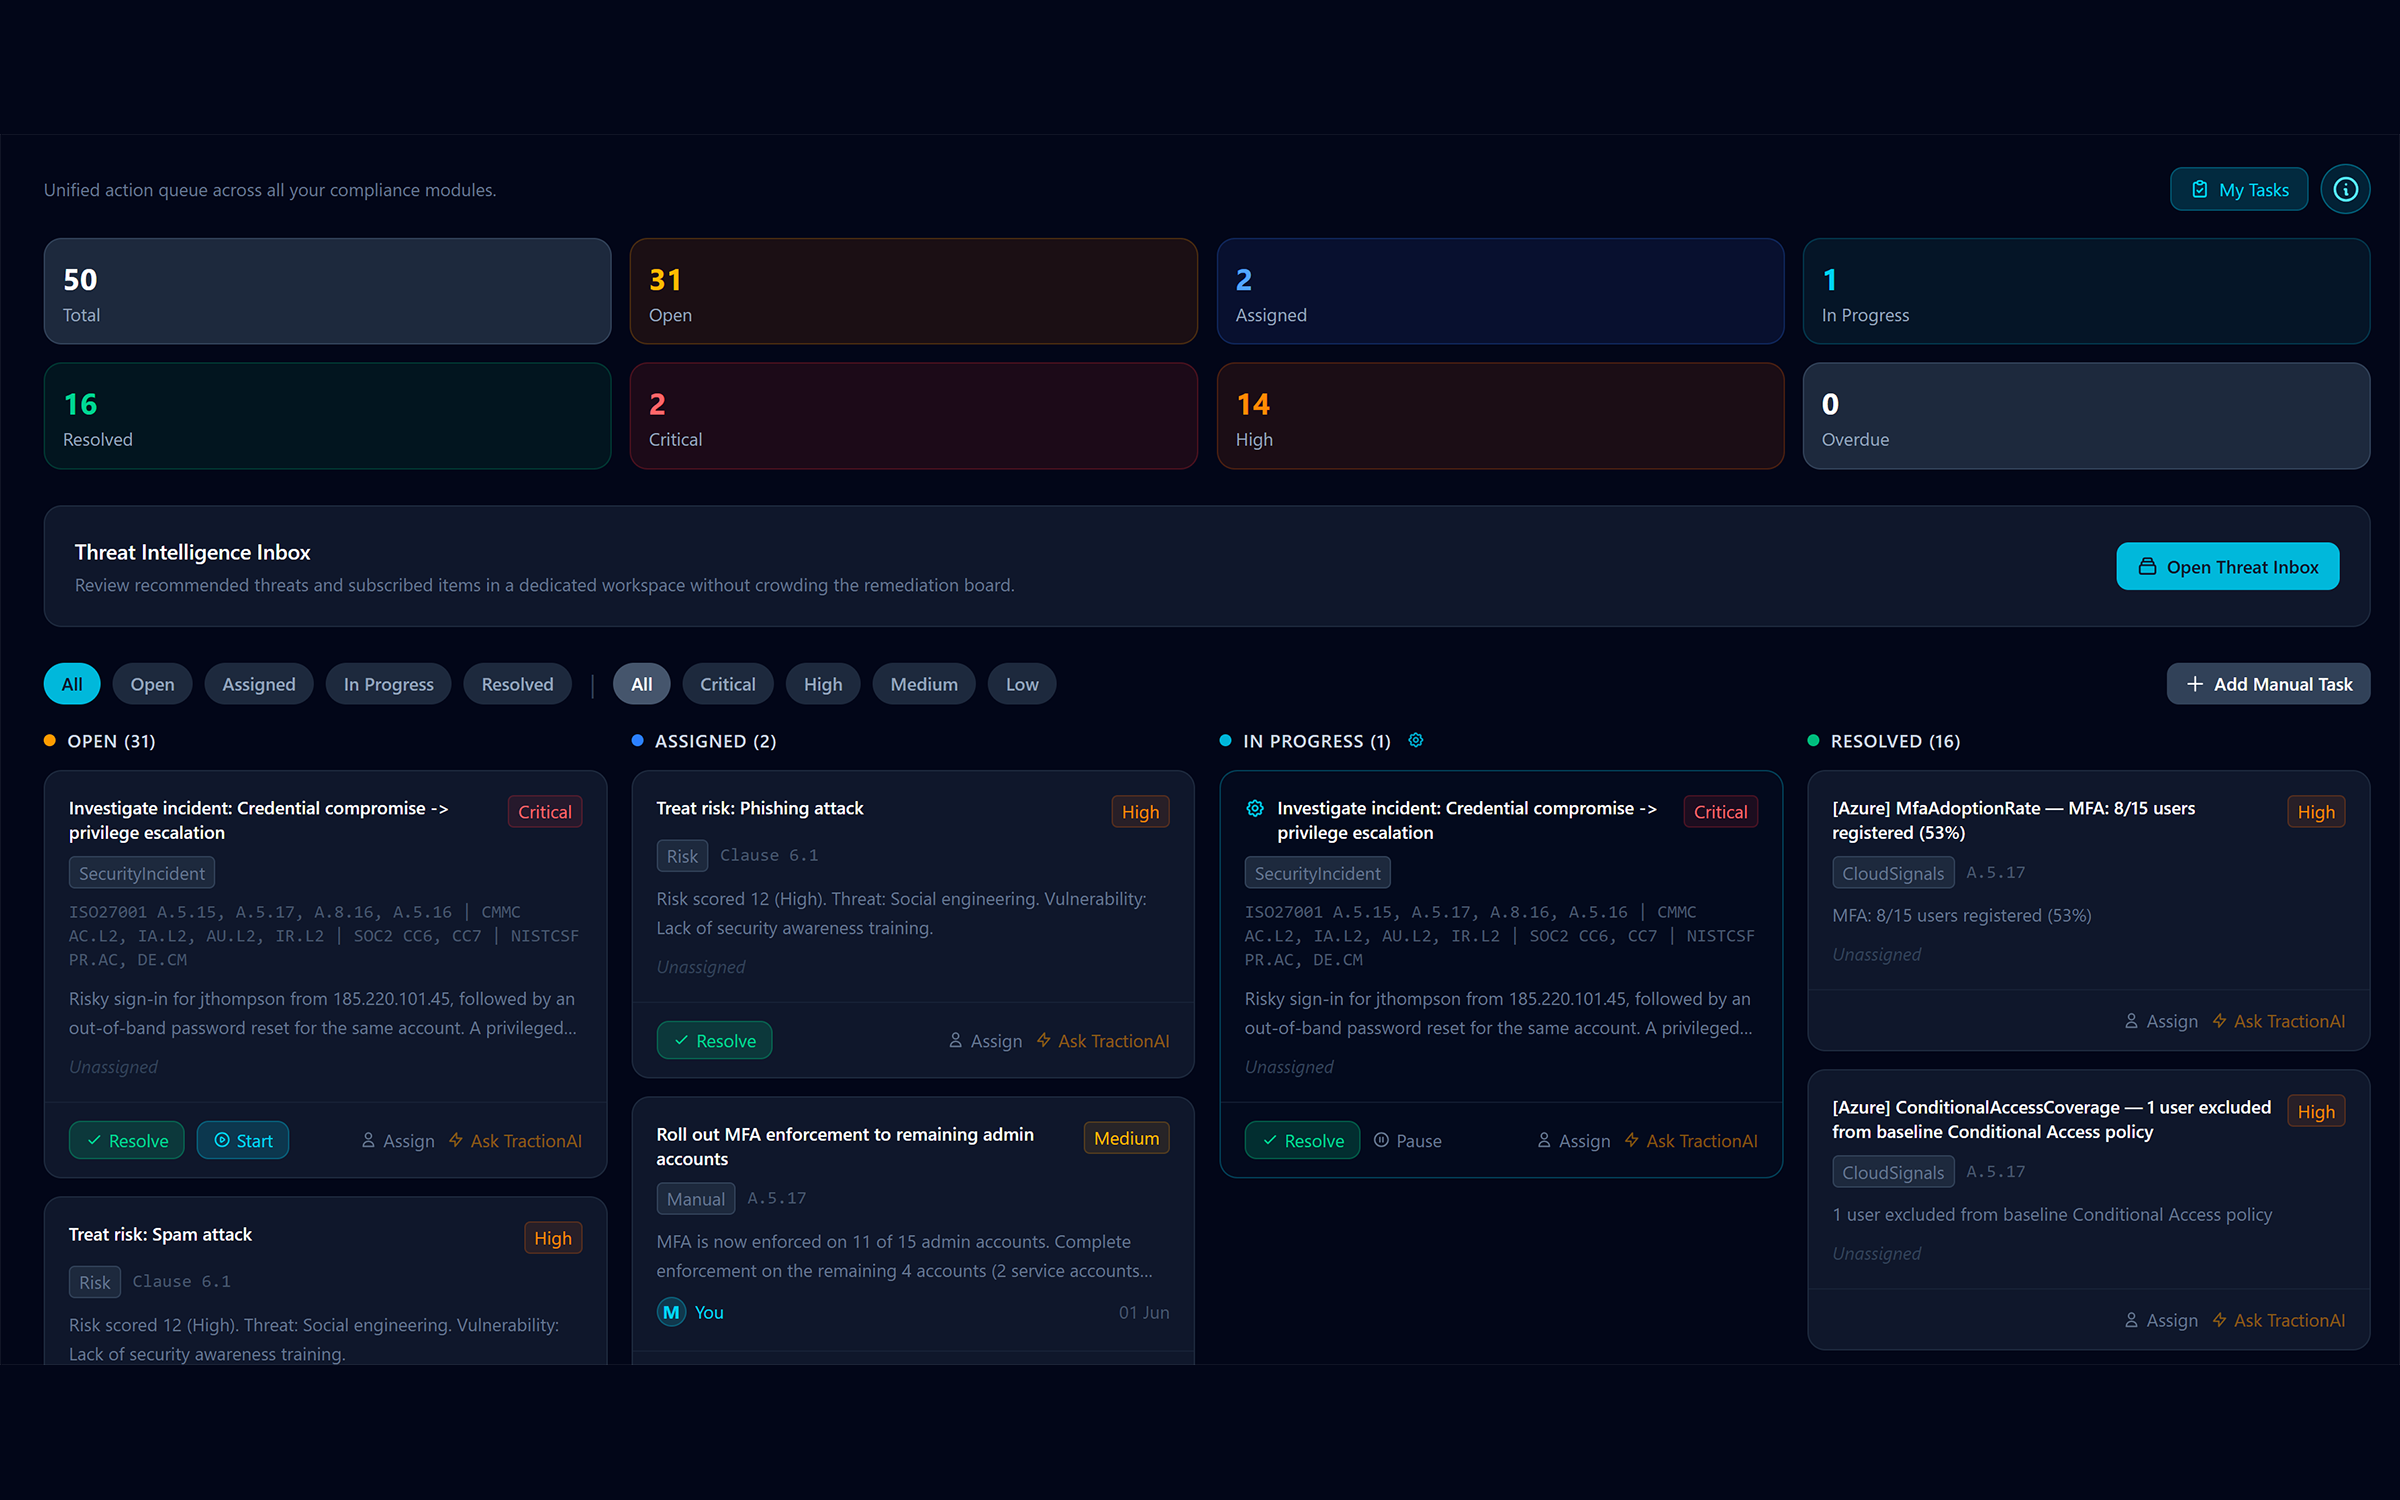
Gaps become tasks
Gaps you find and failed cloud checks become tasks in one remediation queue, with owners and due dates: the working list behind your plan of action.
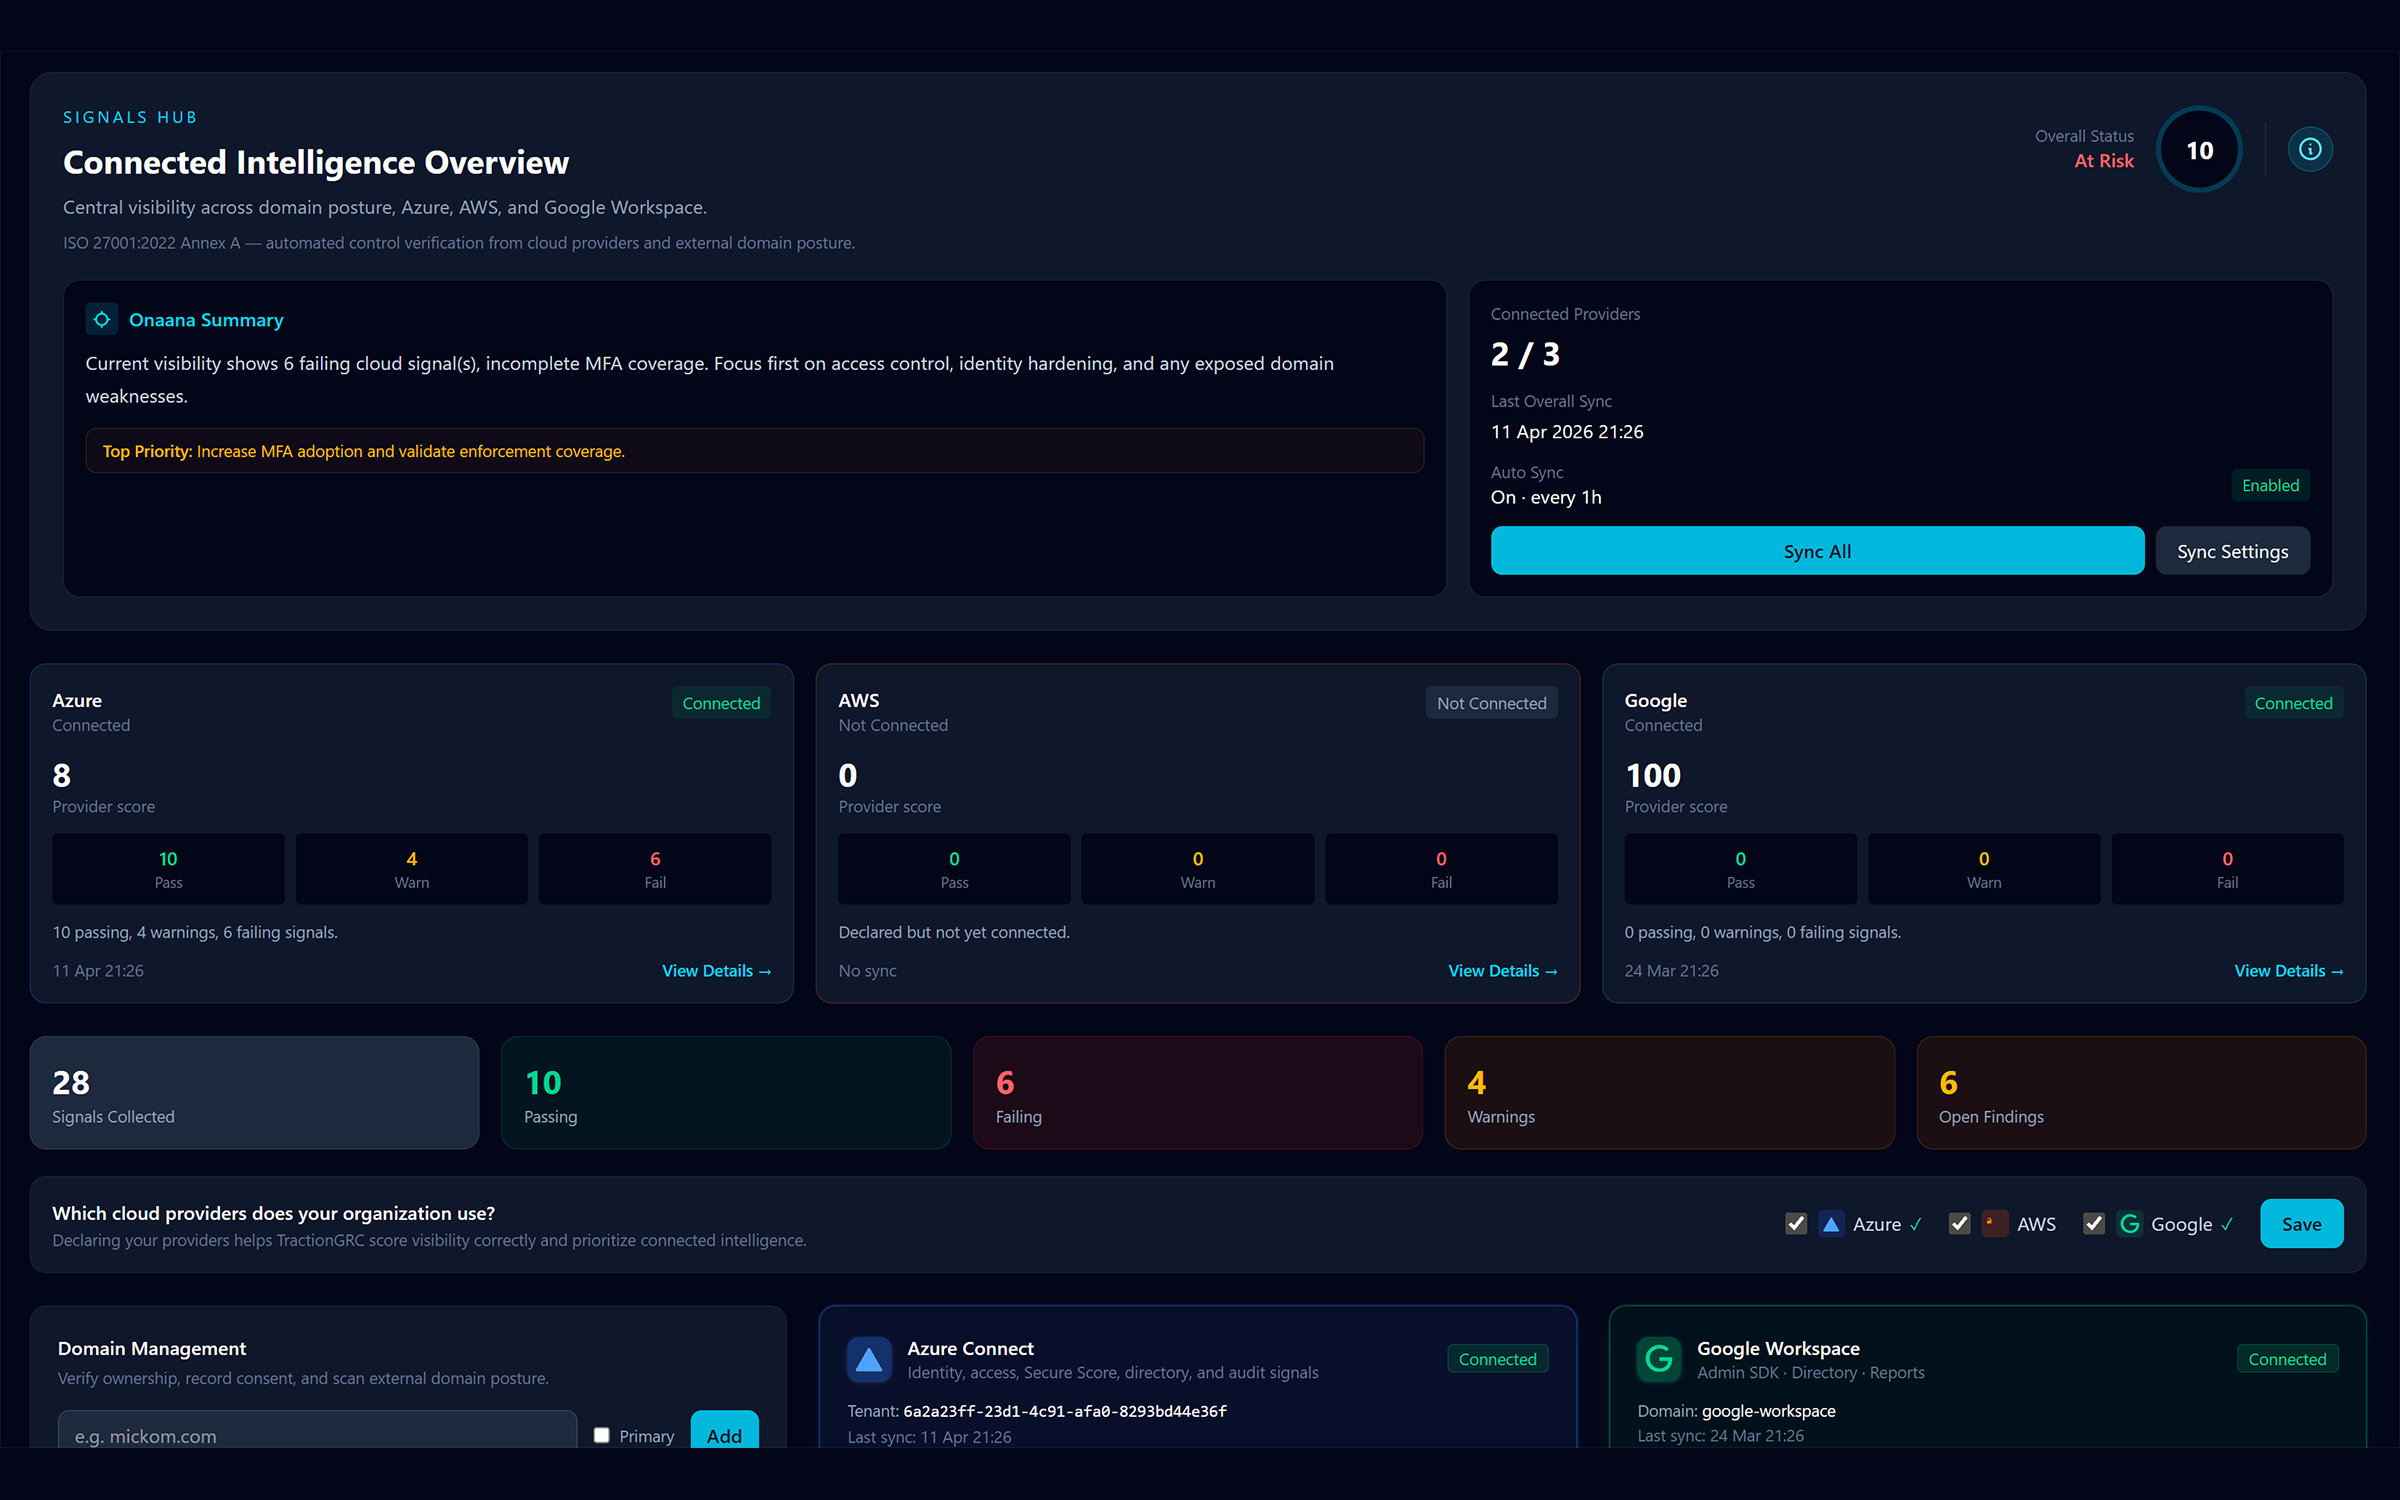
Cloud checks every hour
Read-only connections to Azure and Google Workspace (Starter and up) and AWS (Professional and up) check settings such as MFA and logging automatically.
Suppliers and subcontractors
Keep a supplier register with each supplier's TractionScore, and on Professional send your subcontractors assurance questionnaires from the starter libraries.
One score for leadership
TractionScore rolls documentation, risk, controls, operations, audit and cloud signals into one 0 to 100 number, so you can show progress to leadership or a prime.
How the work runs
-
Set your scope
Decide which people, systems and locations handle FCI or CUI. A tight boundary is the single biggest lever on how much work Level 2 takes.
-
Start with Level 1
The 17 practices are the base of Level 2 as well. Post your Level 1 self-assessment and affirmation while you build out the rest.
-
Work through the 110 requirements
Assign owners, connect your cloud accounts, approve the policies, and attach evidence. If you already run ISO 27001, start from the mapped controls.
-
Score yourself and close gaps
Use the DoD Assessment Methodology to score each requirement, track what is left as tasks, and post your score in SPRS.
-
Keep it current
Affirm every year, and keep evidence current between assessments so you are ready when Phase 2 resumes or a prime asks.
Timing depends on your scope and on how much is already in place. Level 1 is a much smaller job than Level 2, and an existing ISO 27001 program shortens Level 2.
Where TractionGRC fits
TractionGRC is where you run your CMMC program. A few parts of the work sit with your own environment or with other partners, and the platform is built to work alongside them.
Assessments
Your team performs the self-assessment, or an authorized C3PAO does when a contract requires it. TractionGRC helps you prepare for both, with your practices, evidence and gaps in one place.
Your CUI
CUI stays in your own approved environment. TractionGRC holds your program records: practices, owners, evidence, policies and tasks.
Cloud connections
Automatic checks cover Azure, Google Workspace and AWS. If you run Microsoft GCC High, you can add evidence from it by upload.
SPRS, SSP and POA&M
You can record your SPRS details in TractionGRC and track the content behind your SSP and POA&M: scope, practices, gaps, owners and dates. A System Security Plan builder is on our roadmap.
FedRAMP
FedRAMP authorization is on our roadmap.
Plans
CMMC Level 1 is on Starter ($349 a month), Level 2 on Professional ($999 a month), and Level 3 on Enterprise, priced per customer. Annual billing gives you two months free. You can start on the Free plan with NIST CSF and CIS Controls and move up when a contract needs it.
CMMC questions
Is CMMC Phase 2 still happening?
Phase 2 was suspended on July 13, 2026 while DoD reviews the program, and no restart date has been set. The CMMC rule itself (32 CFR Part 170) was not repealed. Under DFARS Class Deviation 2026-O0025 (Revision 3, September 3, 2026), solicitations accept Level 1 and Level 2 self-assessments, and the CMMC clause becomes automatic in new contracts involving FCI or CUI from November 10, 2028. Last checked October 29, 2026.
Is a Level 2 self-assessment enough today?
For most current DoD solicitations, yes: while Phase 2 is suspended, contracts designate Level 1 or Level 2 self-assessments, not C3PAO assessments. The self-assessment still has to be accurate. You score yourself against the 110 requirements of NIST SP 800-171 Rev 2, post the score in SPRS, and affirm it, and that affirmation is a representation to the government. Third-party assessments are expected to return when Phase 2 resumes, so check each solicitation.
Do subcontractors need CMMC?
Yes. CMMC requirements flow down under DFARS 252.204-7021. A subcontractor that processes, stores, or transmits the prime's CUI needs the same level for that scope, and one that handles only FCI needs Level 1. Small suppliers are in scope, not just large primes.
What is an SPRS score?
SPRS (Supplier Performance Risk System) is the DoD system where contractors post their NIST SP 800-171 self-assessment results. The DoD Assessment Methodology starts at 110 and subtracts points for each requirement not yet implemented, so a score can fall below zero. DFARS 252.204-7019 requires a current score in SPRS, and CMMC adds an annual affirmation by a senior official.
Can I use ISO 27001 work for CMMC?
Yes, as a head start. In TractionGRC every CMMC requirement, at all three levels, is mapped to its closest ISO 27001:2022 Annex A control, so controls and evidence from an ISO 27001 program show up against CMMC. How much carries over depends on your scope: requirements specific to CUI, such as marking, media protection and the CUI boundary, still need their own work.
How does TractionGRC work with a C3PAO?
TractionGRC is where you run the program day to day: practices, owners, evidence, policies, gaps and readiness. Assessments are performed by your own team or, when a contract requires it, by an authorized C3PAO, and TractionGRC helps you arrive prepared with your records in one place. TractionGRC itself is a software platform, not an assessor.
More answers on the FAQ page, in CMMC Phase 2 suspended: what still applies, and in the CMMC Level 2 cost guide.
Sources
- 32 CFR Part 170, the CMMC program rule
- 32 CFR 170.15, CMMC Level 1 requirements
- Federal News Network: Pentagon suspends CMMC Phase 2 and launches a review (July 2026)
- Kiteworks: DFARS Class Deviation 2026-O0025, Revision 3
- NCMBC: CMMC updates, what still applies during the suspension
- Federal News Network: RFI offers path forward for DoD with CMMC (October 2026)
- NIST SP 800-171 Rev 2
- SPRS (Supplier Performance Risk System)